|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0682: php Vulnerability Assessment Details
|
RHSA-2006-0682: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment Updated PHP packages that fix multiple security issues are now available for Red Hat Enterprise Linux 2.1. This update has been rated as having moderate security impact by the Red Hat Security Response Team. PHP is an HTML-embedded scripting language commonly used with the Apache HTTP Web server. A response-splitting issue was discovered in the PHP session handling. If a remote attacker can force a carefully crafted session identifier to be used, a cross-site-scripting or response-splitting attack could be possible. (CVE-2006-3016) A buffer overflow was discovered found in the PHP sscanf() function. If a script used the sscanf() function with positional arguments in the format string, a remote attacker sending a carefully crafted request could execute arbitrary code as the 'apache' user. (CVE-2006-4020) An integer overflow was discovered in the PHP wordwrap() and str_repeat() functions. If a script running on a 64-bit server used either of these functions on untrusted user data, a remote attacker sending a carefully crafted request might be able to cause a heap overflow. (CVE-2006-4482) An integer overflow was discovered in the PHP memory allocation handling. On 64-bit platforms, the "memory_limit" setting was not enforced correctly, which could permit a denial of service attack by a remote user. (CVE-2006-4486) Users of PHP should upgrade to these updated packages which contain backported patches to correct these issues. These packages also contain a fix for a bug where certain input strings to the metaphone() function could cause memory corruption. Solution : http://rhn.redhat.com/errata/RHSA-2006-0682.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Genuine IBM ThinkPad Trackpoint Tip Cap Pack 91P8421 NEW OLD STOCK -SEALED - OEM
$8.88
Vintage IBM 5140 PC Convertible Power Supply AC Adapter Charger 2684292 OEM
$39.99
2025 NEW Genuine OEM BATTERY for IBM 00Y4643 00Y4594 90Y7689 90Y7632 V3700 V3500
$119.00
IBM 5763-SS1 R02M00 AS/400 Cumulative PTFS Operating System/400 V3 LOT 6 OEM New
$999.99
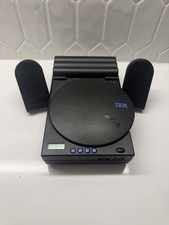
IBM OEM Genuine 1969-009 CD Driver Untested As PARTS. Read Description.
$32.99
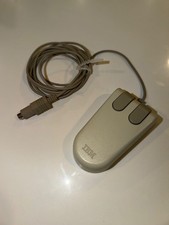
IBM 6450350 OEM PS/2 2-Button Ball Mouse NEW NOS Made in Japan
$19.99
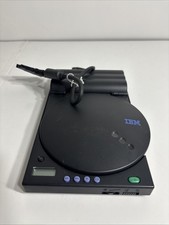
IBM OEM Genuine 1969-010 CD Driver Untested
$40.49
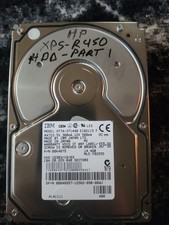
IBM OEM Model DTTA-371440 14.4 GB 12V 500 A
$70.00
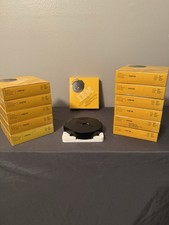
Lot of 12 Genuine IBM 1299790 Quietwriter Non-Correcting Ribbons Indelible NOS
$129.99
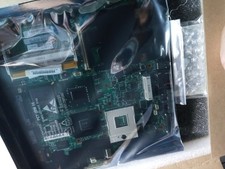
NEW IBM Lenovo T61 14in 4;3 NOT WIDE motherboard T601F FRANKENPAD 44C3924 OEM
$299.95
|
||
|
No Discussions have been posted on this vulnerability. |