|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0675: firefox Vulnerability Assessment Details
|
RHSA-2006-0675: firefox |
||
|
Check for the version of the firefox packages Detailed Explanation for this Vulnerability Assessment Updated firefox packages that fix several security bugs are now available for Red Hat Enterprise Linux 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. Mozilla Firefox is an open source Web browser. Two flaws were found in the way Firefox processed certain regular expressions. A malicious web page could crash the browser or possibly execute arbitrary code as the user running Firefox. (CVE-2006-4565, CVE-2006-4566) A number of flaws were found in Firefox. A malicious web page could crash the browser or possibly execute arbitrary code as the user running Firefox. (CVE-2006-4571) A flaw was found in the handling of Javascript timed events. A malicious web page could crash the browser or possibly execute arbitrary code as the user running Firefox. (CVE-2006-4253) Daniel Bleichenbacher recently described an implementation error in RSA signature verification. For RSA keys with exponent 3 it is possible for an attacker to forge a signature that would be incorrectly verified by the NSS library. Firefox as shipped trusts several root Certificate Authorities that use exponent 3. A possible hacker could have created a carefully crafted SSL certificate which be incorrectly trusted when their site was visited by a victim. (CVE-2006-4340) A flaw was found in the Firefox auto-update verification system. An attacker who has the ability to spoof a victim's DNS could get Firefox to download and install malicious code. In order to exploit this issue an attacker would also need to get a victim to previously accept an unverifiable certificate. (CVE-2006-4567) Firefox did not properly prevent a frame in one domain from injecting content into a sub-frame that belongs to another domain, which facilitates website spoofing and other attacks (CVE-2006-4568) Firefox did not load manually opened, blocked popups in the right domain context, which could lead to cross-site scripting attacks. In order to exploit this issue a possible hacker would need to find a site which would frame their malicious page and convince the user to manually open a blocked popup. (CVE-2006-4569) Users of Firefox are advised to upgrade to this update, which contains Firefox version 1.5.0.7 that corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0675.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

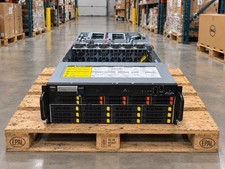
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
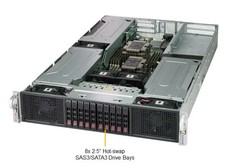
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |