|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0602: wireshark Vulnerability Assessment Details
|
RHSA-2006-0602: wireshark |
||
|
Check for the version of the wireshark packages Detailed Explanation for this Vulnerability Assessment New Wireshark packages that fix various security vulnerabilities in Ethereal are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. Ethereal is a program for monitoring network traffic. In May 2006, Ethereal changed its name to Wireshark. This update deprecates the Ethereal packages in Red Hat Enterprise Linux 2.1, 3, and 4 in favor of the supported Wireshark packages. Several denial of service bugs were found in Ethereal's protocol dissectors. It was possible for Ethereal to crash or stop responding if it read a malformed packet off the network. (CVE-2006-3627, CVE-2006-3629, CVE-2006-3631) Several buffer overflow bugs were found in Ethereal's ANSI MAP, NCP NMAS, and NDPStelnet dissectors. It was possible for Ethereal to crash or execute arbitrary code if it read a malformed packet off the network. (CVE-2006-3630, CVE-2006-3632) Several format string bugs were found in Ethereal's Checkpoint FW-1, MQ, XML, and NTP dissectors. It was possible for Ethereal to crash or execute arbitrary code if it read a malformed packet off the network. (CVE-2006-3628) Users of Ethereal should upgrade to these updated packages containing Wireshark version 0.99.2, which is not vulnerable to these issues Solution : http://rhn.redhat.com/errata/RHSA-2006-0602.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
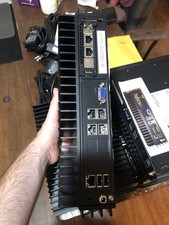
Supermicro SYS-E302-9A Fanless Firewall Atom C3558 16GB ECC 64GB SSD 6x GbE i350
$325.00
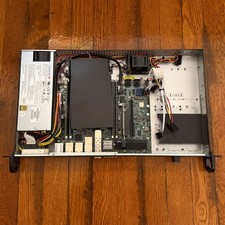
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
1U Edge Firewall Server X11SCW-F Xeon E-2174G 0 RAM M.2 NVME 3x PCI-e 2x PSU X
$175.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
$280.00
|
||
|
No Discussions have been posted on this vulnerability. |