|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0582: kdebase Vulnerability Assessment Details
|
RHSA-2006-0582: kdebase |
||
|
Check for the version of the kdebase packages Detailed Explanation for this Vulnerability Assessment Updated kdebase packages that resolve several bugs are now available. This update has been rated as having low security impact by the Red Hat Security Response Team. The kdebase packages provide the core applications for KDE, the K Desktop Environment. These core packages include the file manager Konqueror. Ilja van Sprundel discovered a lock file handling flaw in kcheckpass. If the directory /var/lock is writable by a user who is permited to run kcheckpass, that user could gain root rights. In Red Hat Enterprise Linux, the /var/lock directory is not writable by users and therefore this flaw could only have been exploited if the permissions on that directory have been badly configured. A patch to block this issue has been included in this update. (CVE-2005-2494) The following bugs have also been addressed: - kstart --tosystray does not send the window to the system tray in Kicker - When the customer enters or selects URLs in Firefox's address field, the desktop freezes for a couple of seconds - fish kioslave is broken on 64-bit systems All users of kdebase should upgrade to these updated packages, which contain patches to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0582.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

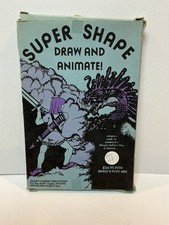
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
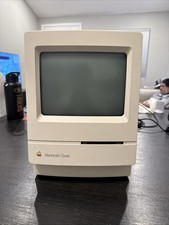
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
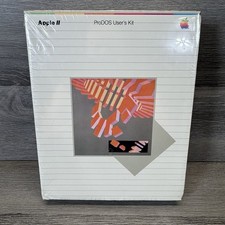
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
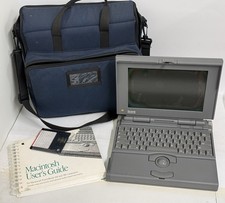
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
Vintage Apple Mac A1048 White Wired Full Size Keyboard w/ 2 USB Ports TESTED
$29.00
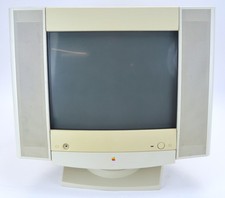
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
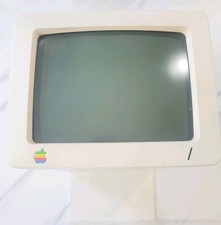
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |