|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0573: openoffice.org Vulnerability Assessment Details
|
RHSA-2006-0573: openoffice.org |
||
|
Check for the version of the openoffice.org packages Detailed Explanation for this Vulnerability Assessment Updated openoffice.org packages are now available. This update has been rated as having important security impact by the Red Hat Security Response Team. OpenOffice.org is an office productivity suite that includes desktop applications such as a word processor, spreadsheet, presentation manager, formula editor, and drawing program. A Sun security specialist reported an issue with the application framework. A possible hacker could put macros into document locations that could cause OpenOffice.org to execute them when the file was opened by a victim. (CVE-2006-2198) A bug was found in the OpenOffice.org Java virtual machine implementation. A possible hacker could write a carefully crafted Java applet that can break through the "sandbox" and have full access to system resources with the current user rights. (CVE-2006-2199) A buffer overflow bug was found in the OpenOffice.org file processor. An attacker could create a carefully crafted XML file that could cause OpenOffice.org to write data to an arbitrary location in memory when the file was opened by a victim. (CVE-2006-3117) All users of OpenOffice.org are advised to upgrade to these updated packages, which contain backported fixes for these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0573.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Lenovo ThinkPad E14 Gen 2 Laptop 14” HD Ryzen 5 16GB RAM 512GB SSD Win 11 Pro
$334.99
Lenovo ThinkPad E14 Gen 3 Laptop 14” FHD AMD Ryzen 5 16GB RAM 512GB SSD Win 11
$374.99
Lenovo Thinkbook 14s Yoga ITL 14” Core i7-1165G7, 16GB RAM, 512GB SSD Touch
$379.00
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
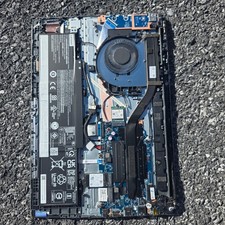
Lenovo IdeaPad Slim 3x 15Q8X10 83N30010US 16GB 1TB SSD keybord Parts/Repair
$190.00
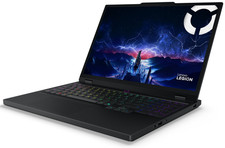
Lenovo Legion 5 Gaming 15.1" WQXGA OLED 165Hz Core i9-14900HX 16GB 1TB RTX 5070
$1469.00
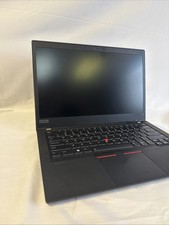
Lenovo ThinkPad T14 Gen 1 14" AMD Ryzen 5 16GB 256GB SSD
$219.99
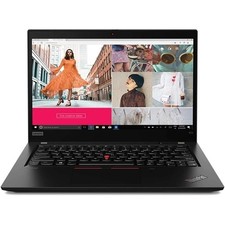
Lenovo ThinkPad X13 Gen 1 i5-10310U 16GB 512GB SSD Touch Win 11 Pro Good
$222.99
Lenovo ThinkPad L15 Gen 3 15.6" 16GB, Thunder Black
$241.50
Lenovo ThinkPad T14s Laptop 14” Laptop Core i5 8GB RAM 256GB SSD Windows 11 Pro
$249.99
|
||
|
No Discussions have been posted on this vulnerability. |