|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0526: rh-postgres Vulnerability Assessment Details
|
RHSA-2006-0526: rh-postgres |
||
|
Check for the version of the rh packages Detailed Explanation for this Vulnerability Assessment Updated postgresql packages that fix several security vulnerabilities are now available for Red Hat Enterprise Linux 3 and 4. This update has been rated as having important security impact by the Red Hat Security Response Team. PostgreSQL is an advanced Object-Relational database management system (DBMS). A bug was found in the way PostgreSQL's PQescapeString function escapes strings when operating in a multibyte character encoding. It is possible for a possible hacker to provide an application a carefully crafted string containing invalidly-encoded characters, which may be improperly escaped, permiting the attacker to inject malicious SQL. While this update fixes how PQescapeString operates, the PostgreSQL server has also been modified to prevent such an attack occurring through unpatched clients. (CVE-2006-2313, CVE-2006-2314). More details about this issue are available in the linked PostgreSQL technical documentation. An integer signedness bug was found in the way PostgreSQL generated password salts. The actual salt size is only half the size of the expected salt, making the process of brute forcing password hashes slightly easier. This update will not strengthen already existing passwords, but all newly assigned passwords will have the proper salt length. (CVE-2006-0591) Users of PostgreSQL should upgrade to these updated packages containing PostgreSQL version 7.4.13, which corrects these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0526.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
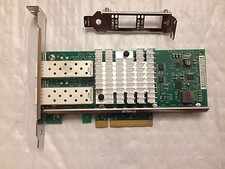
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |