|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0501: php Vulnerability Assessment Details
|
RHSA-2006-0501: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment Updated PHP packages that fix multiple security issues are now available for Red Hat Enterprise Linux 2.1. This update has been rated as having moderate security impact by the Red Hat Security Response Team. PHP is an HTML-embedded scripting language commonly used with the Apache HTTP Web server. The phpinfo() PHP function did not properly sanitize long strings. An attacker could use this to perform cross-site scripting attacks against sites that have publicly-available PHP scripts that call phpinfo(). (CVE-2006-0996) The error handling output was found to not properly escape HTML output in certain cases. A possible hacker could use this flaw to perform cross-site scripting attacks against sites where both display_errors and html_errors are enabled. (CVE-2006-0208) A buffer overflow flaw was discovered in uw-imap, the University of Washington's IMAP Server. php-imap is compiled against the static c-client libraries from imap and therefore needed to be recompiled against the fixed version. (CVE-2005-2933) The wordwrap() PHP function did not properly check for integer overflow in the handling of the "break" parameter. A possible hacker who could control the string passed to the "break" parameter could cause a heap overflow. (CVE-2006-1990) Users of PHP should upgrade to these updated packages, which contain backported patches that resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0501.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

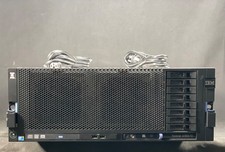
IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
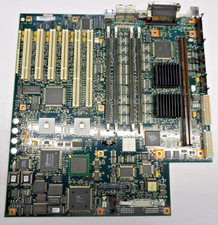
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
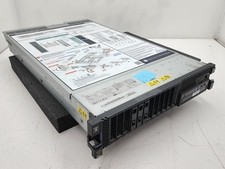
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
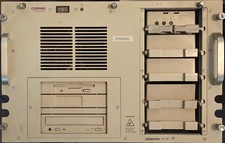
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
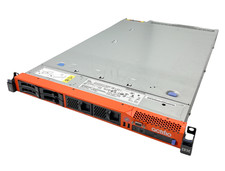
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00

IBM 4262 SYSTEM x3200 Tower - HDD Wiped, NO OS
$80.00
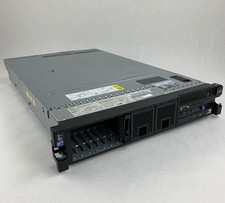
IBM System X3650 M3 Server Xeon E5620 2.4 GHz 16 GB Ram Raid M5015 No OS No HDD
$87.96
IBM 00FN709 X3850 X6 Compute Book 3837 Barebone
$114.99
|
||
|
No Discussions have been posted on this vulnerability. |