|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0330: thunderbird Vulnerability Assessment Details
|
RHSA-2006-0330: thunderbird |
||
|
Check for the version of the thunderbird packages Detailed Explanation for this Vulnerability Assessment An updated thunderbird package that fixes various bugs is now available for Red Hat Enterprise Linux 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. Mozilla Thunderbird is a standalone mail and newsgroup client. Several bugs were found in the way Thunderbird processes malformed javascript. A malicious HTML mail message could modify the content of a different open HTML mail message, possibly stealing sensitive information or conducting a cross-site scripting attack. Please note that JavaScript support is disabled by default in Thunderbird. (CVE-2006-1731, CVE-2006-1732, CVE-2006-1741) Several bugs were found in the way Thunderbird processes certain javascript actions. A malicious HTML mail message could execute arbitrary javascript instructions with the permissions of 'chrome', permiting the page to steal sensitive information or install browser malware. Please note that JavaScript support is disabled by default in Thunderbird. (CVE-2006-0292, CVE-2006-0296, CVE-2006-1727, CVE-2006-1728, CVE-2006-1733, CVE-2006-1734, CVE-2006-1735, CVE-2006-1742) Several bugs were found in the way Thunderbird processes malformed HTML mail messages. A carefully crafted malicious HTML mail message could cause the execution of arbitrary code as the user running Thunderbird. (CVE-2006-0749, CVE-2006-1724, CVE-2006-1730, CVE-2006-1737, CVE-2006-1738, CVE-2006-1739, CVE-2006-1790) A bug was found in the way Thunderbird processes certain inline content in HTML mail messages. It may be possible for a remote attacker to send a carefully crafted mail message to the victim, which will fetch remote content, even if Thunderbird is configured not to fetch remote content. (CVE-2006-1045) Users of Thunderbird are advised to upgrade to this updated package containing Thunderbird version 1.0.8, which is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0330.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

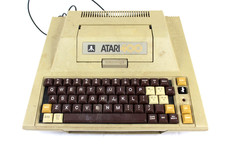
VTG Atari 400 Home Computer System ** Sold "AS-IS" for Parts or Repair
$88.75
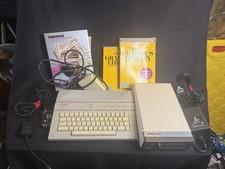
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
DEFECTIVE Atari 810 Vintage Computer Disk Drive powers on Unit Only Boo G3D
$49.29
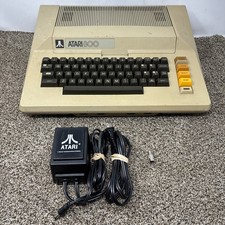
Atari 800 8-bit Computer System Fully Tested Great Condition 48k READ
$350.00
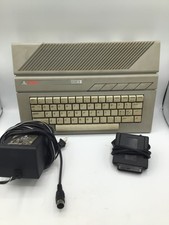
Atari XE 130XE Computer NTSC with Power Supply Powers On Untested
$159.95
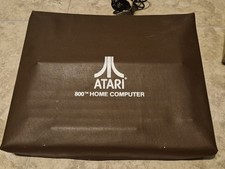
Retro ATARI 800 Computer w/ATARI 410, INDUS G.T., 41x Floppy programs + Cover
$1000.00
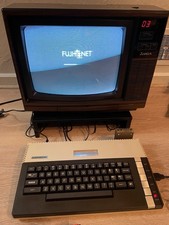
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
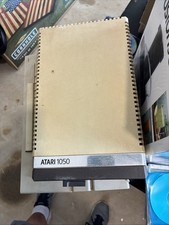
Atari 1050 Floppy Disk Drive with Power Supply, MPN C061636 (Vintage)
$80.00
UNOCART-2600 SD card Multi Rom Cartridge for ATARI 2600 with CASE
$34.25
Vintage Atari SF354 Floppy Disk Drive & Power Supply FOR PARTS OR REPAIR AS IS
$120.00
|
||
|
No Discussions have been posted on this vulnerability. |