|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0266: gnupg Vulnerability Assessment Details
|
RHSA-2006-0266: gnupg |
||
|
Check for the version of the gnupg packages Detailed Explanation for this Vulnerability Assessment An updated GnuPG package that fixes signature verification flaws as well as minor bugs is now available. This update has been rated as having important security impact by the Red Hat Security Response Team. GnuPG is a utility for encrypting data and creating digital signatures. Tavis Ormandy discovered a bug in the way GnuPG verifies cryptographically signed data with detached signatures. It is possible for a possible hacker to construct a cryptographically signed message which could appear to come from a third party. When a victim processes a GnuPG message with a malformed detached signature, GnuPG ignores the malformed signature, processes and outputs the signed data, and exits with status 0, just as it would if the signature had been valid. In this case, GnuPG's exit status would not indicate that no signature verification had taken place. This issue would primarily be of concern when processing GnuPG results via an automated script. The Common Vulnerabilities and Exposures project assigned the name CVE-2006-0455 to this issue. Tavis Ormandy also discovered a bug in the way GnuPG verifies cryptographically signed data with inline signatures. It is possible for an attacker to inject unsigned data into a signed message in such a way that when a victim processes the message to recover the data, the unsigned data is output along with the signed data, gaining the appearance of having been signed. This issue is mitigated in the GnuPG shipped with Red Hat Enterprise Linux as the --ignore-crc-error option must be passed to the gpg executable for this attack to be successful. The Common Vulnerabilities and Exposures project assigned the name CVE-2006-0049 to this issue. Please note that neither of these issues affect the way RPM or up2date verify RPM package files, nor is RPM vulnerable to either of these issues. All users of GnuPG are advised to upgrade to this updated package, which contains backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0266.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

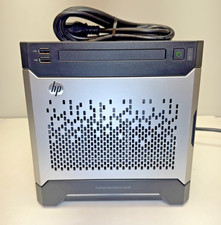
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
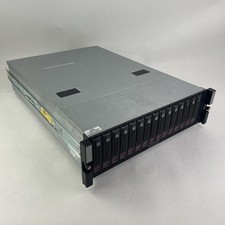
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
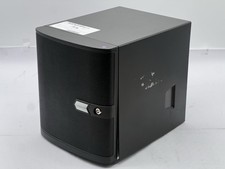
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro CSE-815-5 4B LFF Xeon E3-1245v6 16GB DDR4 1x 9361-8i 4x 1TB SATA HDD
$483.99
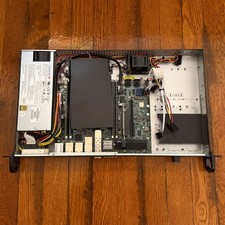
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
$280.00
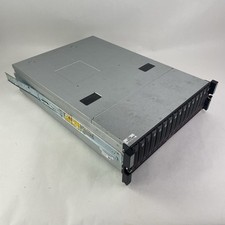
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |