|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0265: sendmail Vulnerability Assessment Details
|
RHSA-2006-0265: sendmail |
||
|
Check for the version of the sendmail packages Detailed Explanation for this Vulnerability Assessment Updated sendmail packages to fix a security issue are now available for Red Hat Enterprise Linux 2.1. This update has been rated as having critical security impact by the Red Hat Security Response Team. Sendmail is a Mail Transport Agent (MTA) used to send mail between machines. A flaw in the handling of asynchronous signals was discovered in Sendmail. A remote attacker may be able to exploit a race condition to execute arbitrary code as root. The Common Vulnerabilities and Exposures project assigned the name CVE-2006-0058 to this issue. By default on Red Hat Enterprise Linux 2.1, Sendmail is configured to only accept connections from the local host. Therefore only users who have configured Sendmail to listen to remote hosts would be able to be remotely exploited by this vulnerability. In order to correct this issue for Red Hat Enterprise Linux 2.1 users, it was necessary to upgrade the version of Sendmail from 8.11 as originally shipped to Sendmail 8.12 with the addition of the security patch supplied by Sendmail Inc. This erratum provides updated packages based on Sendmail 8.12 with a compatibility mode enabled. After updating to these packages, users should pay close attention to their sendmail logs to ensure that the upgrade completed sucessfully. Solution : http://rhn.redhat.com/errata/RHSA-2006-0265.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

Computer Photo History Altair 8800 Philco 212 CDC 6600 DEC PDP-8 Apple 1 UNIVAC
$69.99
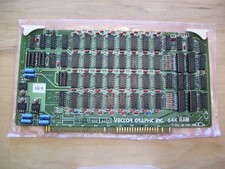
S-100 Vector Graphic 64K Ram Board (Altair, IMSAI)
$99.95
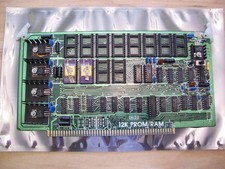
S-100 Vector Graphic 12K PROM/RAM Board (Altair, IMSAI)
$99.95
Microcomputer Builder's Bible IMSAI 8080 Z80 ADM-3A DEC LSI-11 Altair 8800 Bus
$65.00
Vintage Digital Research ZSID 1.4 8" Floppy Disk CP/M Z80 Software S-100 Altair
$69.99
640pg Best of BYTE Magazine 1984 Mac Steve Jobs Altair 8800 IBM 5100 Bob Moog
$85.00
S-100 Industrial Micro Systems 8K Static Ram (IMS, Altair, IMSAI)
$69.95
1979 Microprocessor Projects Altair 8800 Intel 8080 KIM-1 COSMAC Elf SWTPC 6800
$59.99
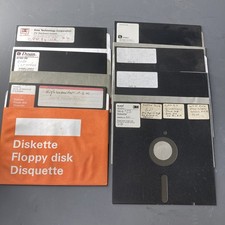
CP/M 86 1.1R 8086 Highmonitor 8 Inch Floppy Diskette 80s IMSAI Altair
$29.99
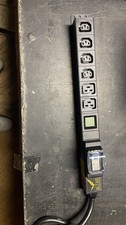
ALTAIR Bitcoin Mining Solutions PDU IEC SERIES 100-250V 30A/24A Power Distribute
$99.00
|
||
|
No Discussions have been posted on this vulnerability. |