|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0132: kernel Vulnerability Assessment Details
|
RHSA-2006-0132: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages are now available as part of ongoing support and maintenance of Red Hat Enterprise Linux version 4. This is the third regular update. This update has been rated as having moderate security impact by the Red Hat Security Response Team. The Linux kernel handles the basic functions of the operating system. This is the third regular kernel update to Red Hat Enterprise Linux 4. New features introduced in this update include: - Open InfiniBand (OpenIB) support - Serial Attached SCSI support - NFS access control lists, asynchronous I/O - IA64 multi-core support and sgi updates - Large SMP CPU limits increased using the largesmp kernel: Up to 512 CPUs in ia64, 128 in ppc64, and 64 in AMD64 and Intel EM64T - Improved read-ahead performance - Common Internet File System (CIFS) update - Error Detection and Correction (EDAC) modules - Unisys support There were several bug fixes in various parts of the kernel. The ongoing effort to resolve these problems has resulted in a marked improvement in the reliability and scalability of Red Hat Enterprise Linux 4. The following security bug was fixed in this update: - dm-crypt did not clear a structure before freeing it, which could permit local users to discover information about cryptographic keys (CVE-2006-0095) The following device drivers have been upgraded to new versions: cciss: 2.6.8 to 2.6.8-rh1 ipmi_devintf: 33.4 to 33.11 ipmi_msghandler: 33.4 to 33.11 ipmi_poweroff: 33.4 to 33.11 ipmi_si: 33.4 to 33.11 ipmi_watchdog: 33.4 to 33.11 mptbase: 3.02.18 to 3.02.60.01rh e1000: 6.0.54-k2-NAPI to 6.1.16-k2-NAPI ixgb: 1.0.95-k2-NAPI to 1.0.100-k2-NAPI tg3: 3.27-rh to 3.43-rh aacraid: 1.1.2-lk2 to 1.1-5[2412] ahci: 1.01 to 1.2 ata_piix: 1.03 to 1.05 iscsi_sfnet: 4:0.1.11-1 to 4:0.1.11-2 libata: 1.11 to 1.20 qla2100: 8.01.00b5-rh2 to 8.01.02-d3 qla2200: 8.01.00b5-rh2 to 8.01.02-d3 qla2300: 8.01.00b5-rh2 to 8.01.02-d3 qla2322: 8.01.00b5-rh2 to 8.01.02-d3 qla2xxx: 8.01.00b5-rh2 to 8.01.02-d3 qla6312: 8.01.00b5-rh2 to 8.01.02-d3 sata_nv: 0.6 to 0.8 sata_promise: 1.01 to 1.03 sata_svw: 1.06 to 1.07 sata_sx4: 0.7 to 0.8 sata_vsc: 1.0 to 1.1 cifs: 1.20 to 1.34 Added drivers: bnx2: 1.4.25 dell_rbu: 0.7 hangcheck-timer: 0.9.0 ib_mthca: 0.06 megaraid_sas: 00.00.02.00 qla2400: 8.01.02-d3 typhoon: 1.5.7 All Red Hat Enterprise Linux 4 users are advised to upgrade their kernels to the packages associated with their machine architectures and configurations as listed in this erratum. Solution : http://rhn.redhat.com/errata/RHSA-2006-0132.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

IBM System X3850-X5 Server w/4x Intel Xeon E7-4870 CPU , 512 GB DDR3 RAM,NO HDD
$1299.99
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$199.99
Unused IBM 09P0037 MAINBOARD For RS/6000 7044-170 P-Series
$375.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$179.99
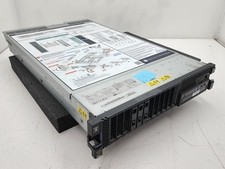
IBM Power 8 S822L Server 8247-22L POWER8 Enterprise 256GB RAM 2x 00KV626 CPU
$999.99
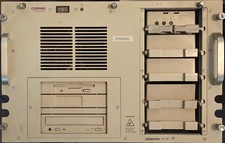
Compaq ProLiant 1500R 5/100 rack server, Series 3155, with IBM 2.1GB HD, VINTAGE
$295.00
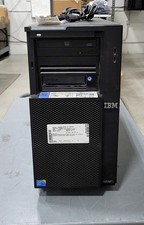
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$110.30
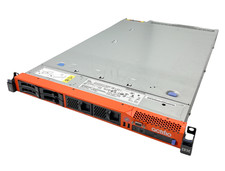
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$150.00
Rare Vintage IBM 93ZZ PowerPC Server Board - MCM Ceramic CPU - 40N1844 - 1.1 lbs
$49.99
Lot of 3 IBM 00JY196 ServeRAID M1210 PCI Express SAS SATA Storage Controller
$68.99
|
||
|
No Discussions have been posted on this vulnerability. |