|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2006-0044: openssh Vulnerability Assessment Details
|
RHSA-2006-0044: openssh |
||
|
Check for the version of the openssh packages Detailed Explanation for this Vulnerability Assessment Updated openssh packages that fix bugs in sshd and add auditing of user logins are now available for Red Hat Enterprise Linux 4. This update has been rated as having low security impact by the Red Hat Security Response Team. OpenSSH is OpenBSD's SSH (Secure SHell) protocol implementation. This package includes the core files necessary for both the OpenSSH client and server. An arbitrary command execution flaw was discovered in the way scp copies files locally. It is possible for a local attacker to create a file with a carefully crafted name that could execute arbitrary commands as the user running scp to copy files locally. The Common Vulnerabilities and Exposures project (cve.mitre.org) assigned the name CVE-2006-0225 to this issue. The following issue has also been fixed in this update: * If the sshd service was stopped using the sshd init script while the main sshd daemon was not running, the init script would kill other sshd processes, such as the running sessions. For example, this could happen when the 'service sshd stop' command was issued twice. Additionally, this update implements auditing of user logins through the system audit service. All users of openssh should upgrade to these updated packages, which resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2006-0044.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2006 Tenable Network Security |
||
|
Cables, Connectors |

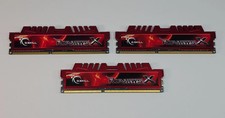
16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
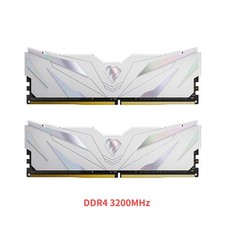
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
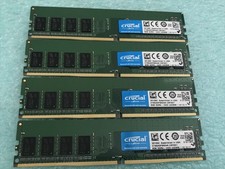
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
Samsung 32GB (2x16GB) DDR5-5600 SODIMM 32GB (2x16GB) PC5-4800 RAM Laptop
$750.00
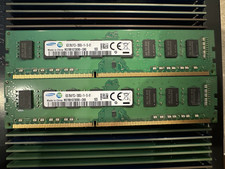
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
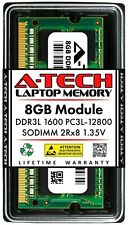
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
Dell 16GB PC4-21300 (DDR4-2666) Memory (SNPPWR5TC16G)
$89.99
|
||
|
No Discussions have been posted on this vulnerability. |