|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-831: php Vulnerability Assessment Details
|
RHSA-2005-831: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment Updated PHP packages that fix multiple security issues are now available for Red Hat Enterprise Linux 3 and 4. This update has been rated as having moderate security impact by the Red Hat Security Response Team. PHP is an HTML-embedded scripting language commonly used with the Apache HTTP Web server. A flaw was found in the way PHP registers global variables during a file upload request. A remote attacker could submit a carefully crafted multipart/form-data POST request that would overwrite the $GLOBALS array, altering expected script behavior, and possibly leading to the execution of arbitrary PHP commands. Please note that this vulnerability only affects installations which have register_globals enabled in the PHP configuration file, which is not a default or recommended option. The Common Vulnerabilities and Exposures project assigned the name CVE-2005-3390 to this issue. A flaw was found in the PHP parse_str() function. If a PHP script passes only one argument to the parse_str() function, and the script can be forced to abort execution during operation (for example due to the memory_limit setting), the register_globals may be enabled even if it is disabled in the PHP configuration file. This vulnerability only affects installations that have PHP scripts using the parse_str function in this way. (CVE-2005-3389) A Cross-Site Scripting flaw was found in the phpinfo() function. If a victim can be tricked into following a malicious URL to a site with a page displaying the phpinfo() output, it may be possible to inject javascript or HTML content into the displayed page or steal data such as cookies. This vulnerability only affects installations which permit users to view the output of the phpinfo() function. As the phpinfo() function outputs a large amount of information about the current state of PHP, it should only be used during debugging or if protected by authentication. (CVE-2005-3388) A denial of service flaw was found in the way PHP processes EXIF image data. It is possible for a possible hacker to cause PHP to crash by supplying carefully crafted EXIF image data. (CVE-2005-3353) Users of PHP should upgrade to these updated packages, which contain backported patches that resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-831.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

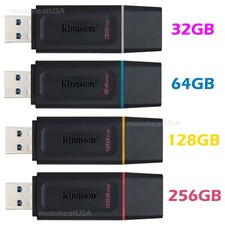
Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.55
24x Micron MT40A512M16LY-062E IT:E 8Gb DDR4-3200 96-FBGA Memory IC
$349.99
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$202.50
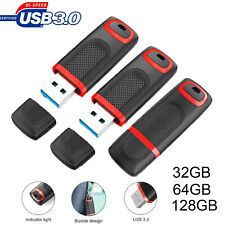
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
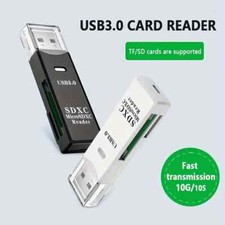
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
Samsung 32GB 2Rx4 DDR4 PC4-2133P M393A4K40BB0-CPB4Q ECC Server Memory Module
$150.00
Server Memory: Samsung 32GB 4DRx4 PC4-2133P ECC LRDIMM DDR4 M386A4G40DM0-CPB
$124.95
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
SK Hynix 32GB DDR4 2133MHz RDIMM Server Memory (HMA84GR7MFR4N-TF) - Preowned
$149.00
|
||
|
No Discussions have been posted on this vulnerability. |