|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-830: openssl Vulnerability Assessment Details
|
RHSA-2005-830: openssl |
||
|
Check for the version of the openssl packages Detailed Explanation for this Vulnerability Assessment Updated OpenSSL096b compatibility packages that fix a remote denial of service vulnerability are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. The OpenSSL toolkit implements Secure Sockets Layer (SSL v2/v3), Transport Layer Security (TLS v1) protocols, and serves as a full-strength general purpose cryptography library. OpenSSL 0.9.6b libraries are provided for Red Hat Enterprise Linux 3 and 4 to permit compatibility with legacy applications. Testing performed by the OpenSSL group using the Codenomicon TLS Test Tool uncovered a null-pointer assignment in the do_change_cipher_spec() function. A remote attacker could perform a carefully crafted SSL/TLS handshake against a server that uses the OpenSSL library in such a way as to cause OpenSSL to crash. Depending on the server this could lead to a denial of service. (CVE-2004-0079) This issue was reported as not affecting OpenSSL versions prior to 0.9.6c, and testing with the Codenomicon Test Tool showed that OpenSSL 0.9.6b as shipped as a compatibility library with Red Hat Enterprise Linux 3 and 4 did not crash. However, an alternative reproducer has been written which shows that this issue does affect versions of OpenSSL prior to 0.9.6c. Note that Red Hat does not ship any applications with Red Hat Enterprise Linux 3 or 4 that use these compatibility libraries. Users of the OpenSSL096b compatibility package are advised to upgrade to these updated packages, which contain a patch provided by the OpenSSL group that protect against this issue. Solution : http://rhn.redhat.com/errata/RHSA-2005-830.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

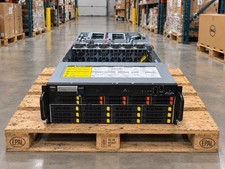
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
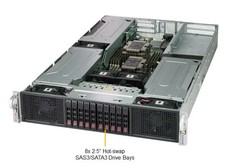
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |