|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-829: openssl Vulnerability Assessment Details
|
RHSA-2005-829: openssl |
||
|
Check for the version of the openssl packages Detailed Explanation for this Vulnerability Assessment Updated OpenSSL packages that fix a remote denial of service vulnerability are now available for Red Hat Enterprise Linux 2.1 This update has been rated as having important security impact by the Red Hat Security Response Team. The OpenSSL toolkit implements Secure Sockets Layer (SSL v2/v3), Transport Layer Security (TLS v1) protocols, and serves as a full-strength general purpose cryptography library. Testing performed by the OpenSSL group using the Codenomicon TLS Test Tool uncovered a null-pointer assignment in the do_change_cipher_spec() function. A remote attacker could perform a carefully crafted SSL/TLS handshake against a server that uses the OpenSSL library in such a way as to cause OpenSSL to crash. Depending on the server this could lead to a denial of service. (CVE-2004-0079) This issue was reported as not affecting OpenSSL versions prior to 0.9.6c, and testing with the Codenomicon Test Tool showed that OpenSSL 0.9.6b as shipped in Red Hat Enterprise Linux 2.1 did not crash. However, an alternative reproducer has been written which shows that this issue does affect versions of OpenSSL prior to 0.9.6c. Users of OpenSSL are advised to upgrade to these updated packages, which contain a patch provided by the OpenSSL group that protects against this issue. NOTE: Because server applications are affected by this issue, users are advised to either restart all services that use OpenSSL functionality or restart their systems after installing these updates. Solution : http://rhn.redhat.com/errata/RHSA-2005-829.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00
Western Digital 0B36404 Ultrastar DC HC320 8TB 7200RPM SATA HDD, HUS728T8TALE6L4
$250.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
Seagate Exos ST20000NM003C 20TB CMR 7200RPM SATA6Gb/s 3.5" Enterprise Hard Drive
$509.99
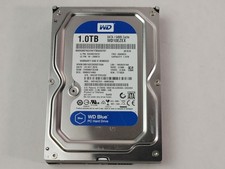
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
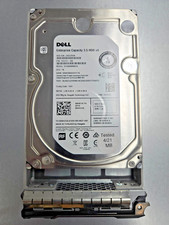
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
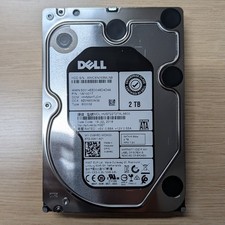
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
|
||
|
No Discussions have been posted on this vulnerability. |