|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-782: losetup Vulnerability Assessment Details
|
RHSA-2005-782: losetup |
||
|
Check for the version of the losetup packages Detailed Explanation for this Vulnerability Assessment Updated util-linux and mount packages that fix two security issues are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. The util-linux package contains a large variety of low-level system utilities that are necessary for a Linux system to function. The mount package contains the mount, umount, swapon and swapoff programs. A bug was found in the way the umount command is executed by normal users. It may be possible for a user to gain elevated rights if the user is able to execute the "umount -r" command on a mounted file system. The file system will be re-mounted only with the "readonly" flag set, clearing flags such as "nosuid" and "noexec". The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-2876 to this issue. This update also fixes a hardlink bug in the script command for Red Hat Enterprise Linux 2.1. If a local user places a hardlinked file named "typescript" in a directory they have write access to, the file will be overwritten if the user running script has write permissions to the destination file. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2001-1494 to this issue. All users of util-linux and mount should upgrade to these updated packages, which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-782.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

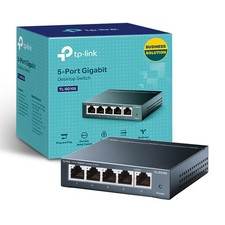
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
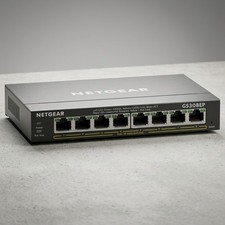
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |