|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-751: nss_ldap Vulnerability Assessment Details
|
RHSA-2005-751: nss_ldap |
||
|
Check for the version of the nss_ldap packages Detailed Explanation for this Vulnerability Assessment Updated openldap and nss_ldap packages that correct a potential password disclosure issue are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. OpenLDAP is an open source suite of LDAP (Lightweight Directory Access Protocol) applications and development tools. The nss_ldap module is an extension for use with GNU libc which permits applications to, without internal modification, consult a directory service using LDAP to supplement information that would be read from local files such as /etc/passwd, /etc/group, and /etc/shadow. A bug was found in the way OpenLDAP, nss_ldap, and pam_ldap refer LDAP servers. If a client connection is referred to a different server, it is possible that the referred connection will not be encrypted even if the client has "ssl start_tls" in its ldap.conf file. The Common Vulnerabilities and Exposures project has assigned the name CVE-2005-2069 to this issue. A bug was also found in the way certain OpenLDAP authentication schemes store hashed passwords. A remote attacker could re-use a hashed password to gain access to unauthorized resources. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-0823 to this issue. All users of OpenLDAP and nss_ldap are advised to upgrade to these updated packages, which contain backported fixes that resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-751.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

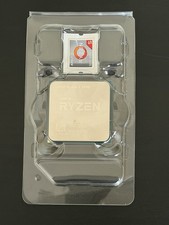
AMD Ryzen 5 5500 Processor ( read Description)
$59.00
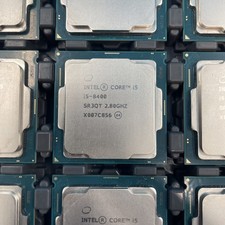
(LOT OF 20) Intel Core i5-8400 CPU 2.80GHz Desktop Processor (SR3QT)
$700.00
INTEL CORE I9-10940X X-SERIES PROCESSOR | 3.30GHZ | SRGSH
$179.99
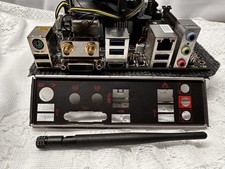
Compo MSI B150I GAMING PRO AC LGA1151 16 Gb DDR4 + Cpu I7 6700+I/O Shields.
$159.00
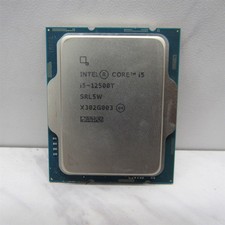
Intel Core i5-12500T SRL5W 2GHz 18MB 6 Core Socket LGA1700 Desktop CPU Processor
$114.99
Intel Core i7-9700 Octa-Core 3 GHz Desktop Processor LGA 1151
$79.99
Intel Core i7-3770K 3.5 GHz Processor
$39.00
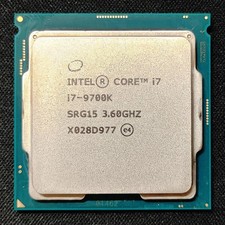
Intel Core i7-9700K Octa-Core 3.6 GHz Desktop CPU
$99.99
Intel Core i7-4770 3.40GHz Quad Core SR149 LGA 1150 CPU Processor tested
$35.00
Lenovo ThinkCentre M920s SFF Barebones PC Motherboard PSU DVD No CPU RAM SSD
$27.99
|
||
|
No Discussions have been posted on this vulnerability. |