|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-709: gdb Vulnerability Assessment Details
|
RHSA-2005-709: gdb |
||
|
Check for the version of the gdb packages Detailed Explanation for this Vulnerability Assessment An updated gdb package that fixes several bugs and minor security issues is now available. This update has been rated as having low security impact by the Red Hat Security Response Team. GDB, the GNU debugger, permits debugging of programs written in C, C++, and other languages by executing them in a controlled fashion, then printing their data. Several integer overflow bugs were found in gdb. If a user is tricked into processing a specially crafted executable file, it may permit the execution of arbitrary code as the user running gdb. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1704 to this issue. A bug was found in the way gdb loads .gdbinit files. When a user executes gdb, the local directory is searched for a .gdbinit file which is then loaded. It is possible for a local user to execute arbitrary commands as the victim running gdb by placing a malicious .gdbinit file in a location where gdb may be run. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1705 to this issue. This updated package also addresses the following issues: - GDB on ia64 had previously implemented a bug fix to work-around a kernel problem when creating a core file via gcore. The bug fix caused a significant slow-down of gcore. - GDB on ia64 issued an extraneous warning when gcore was used. - GDB on ia64 could not backtrace over a sigaltstack. - GDB on ia64 could not successfully do an info frame for a signal trampoline. - GDB on AMD64 and Intel EM64T had problems attaching to a 32-bit process. - GDB on AMD64 and Intel EM64T was not properly handling threaded watchpoints. - GDB could not build with gcc4 when -Werror flag was set. - GDB had problems printing inherited members of C++ classes. - A few updates from mainline sources concerning Dwarf2 partial die in cache support, follow-fork support, interrupted syscall support, and DW_OP_piece read support. All users of gdb should upgrade to this updated package, which resolves these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-709.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
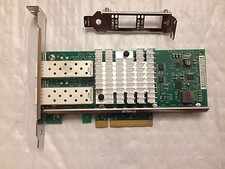
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |