|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-639: kdenetwork Vulnerability Assessment Details
|
RHSA-2005-639: kdenetwork |
||
|
Check for the version of the kdenetwork packages Detailed Explanation for this Vulnerability Assessment Updated kdenetwork packages to correct a security flaw in Kopete are now available for Red Hat Enterprise Linux 4. This update has been rated as having critical security impact by the Red Hat Security Response Team. The kdenetwork package contains networking applications for the K Desktop Environment. Kopete is a KDE instant messenger which supports a number of protocols including ICQ, MSN, Yahoo, Jabber, and Gadu-Gadu. Multiple integer overflow flaws were found in the way Kopete processes Gadu-Gadu messages. A remote attacker could send a specially crafted Gadu-Gadu message which would cause Kopete to crash or possibly execute arbitrary code. The Common Vulnerabilities and Exposures project assigned the name CVE-2005-1852 to this issue. In order to be affected by this issue, a user would need to have registered with Gadu-Gadu and be signed in to the Gadu-Gadu server in order to receive a malicious message. In addition, Red Hat believes that the Exec-shield technology (enabled by default in Red Hat Enterprise Linux 4) would block attempts to remotely exploit this vulnerability. Note that this issue does not affect Red Hat Enterprise Linux 2.1 or 3. Users of Kopete should update to these packages which contain a patch to correct this issue. Solution : http://rhn.redhat.com/errata/RHSA-2005-639.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Cisco Nexus N9K-C92160YC-X 48P 25GbE SFP28 6P QSFP+/QSFP28 PE Switch
$439.00
Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99
Cisco Catalyst C9130AXI-B WiFi 6 802.11ax Wireless Access Point Brand New
$101.99
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99
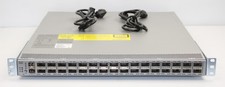
Cisco | N3K-C3232C | 32-Port 100G QSFP Network Switch W/ 2x PSU, 2x Power Cords
$205.00
Cisco C9200-48P-E Cisco POE Network Switch
$749.99

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50
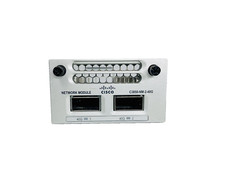
Cisco C3850-NM-2-40G Cisco Catalyst 3850 2x40GE Network Module- Fast Shipping
$269.00
|
||
|
No Discussions have been posted on this vulnerability. |