|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-584: zlib Vulnerability Assessment Details
|
RHSA-2005-584: zlib |
||
|
Check for the version of the zlib packages Detailed Explanation for this Vulnerability Assessment Updated zlib packages that fix a buffer overflow are now available for Red Hat Enterprise Linux 4. This update has been rated as having important security impact by the Red Hat Security Response Team. Zlib is a general-purpose lossless data compression library that is used by many different programs. A previous zlib update, RHSA-2005:569 (CVE-2005-2096) fixed a flaw in zlib that could permit a carefully crafted compressed stream to crash an application. While the original patch corrected the reported overflow, Markus Oberhumer discovered additional ways a stream could trigger an overflow. A possible hacker could create a carefully crafted compressed stream that would cause an application to crash if the stream is opened by a user. As an example, a possible hacker could create a malicious PNG image file that would cause a Web browser or mail viewer to crash if the image is viewed. The Common Vulnerabilities and Exposures project (cve.mitre.org) assigned the name CVE-2005-1849 to this issue. Note that the versions of zlib shipped with Red Hat Enterprise Linux 2.1 and 3 are not vulnerable to this issue. All users should update to these errata packages that contain a patch from Mark Adler that corrects this issue. Solution : http://rhn.redhat.com/errata/RHSA-2005-584.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

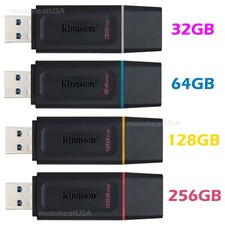
Kingston 32GB 64GB 128GB 256GB USB 3.0 Flash Drive Thumb Memory Stick Pen lot
$285.90
24x Micron MT40A512M16LY-062E IT:E 8Gb DDR4-3200 96-FBGA Memory IC
$349.99
Microsoft Office 2021 Pro Plus USB for 1PC Windows 10 & 11
$62.55
1/ 10/ 100pcs USB 2.0 2GB, 4GB ,8GB ,16GB ,32GB ,64GB 128GB USB Flash Drives Lot
$202.50
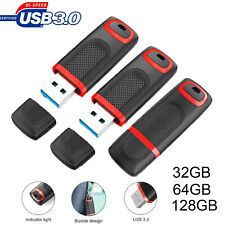
USB 3.0 Flash Drive 32GB 64GB 128GB Memory Stick Thumb Stick Lot Pack
$826.09
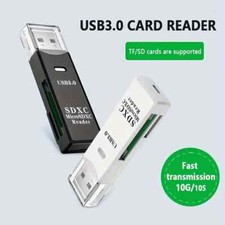
USB 3.0 Micro SD SDHC TF Card Reader Memory Adapter for PC Laptop Camera lot
$3.75
Samsung 32GB 2Rx4 DDR4 PC4-2133P M393A4K40BB0-CPB4Q ECC Server Memory Module
$150.00
Server Memory: Samsung 32GB 4DRx4 PC4-2133P ECC LRDIMM DDR4 M386A4G40DM0-CPB
$124.95
TF/SD Card Adapter Camera Reader Android Type-c For iPhone17 Pro Max Plusm lot
$573.98
SK Hynix 32GB DDR4 2133MHz RDIMM Server Memory (HMA84GR7MFR4N-TF) - Preowned
$149.00
|
||
|
No Discussions have been posted on this vulnerability. |