|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-562: krb Vulnerability Assessment Details
|
RHSA-2005-562: krb |
||
|
Check for the version of the krb packages Detailed Explanation for this Vulnerability Assessment Updated krb5 packages which fix multiple security issues are now available for Red Hat Enterprise Linux 2.1 and 3. This update has been rated as having critical security impact by the Red Hat Security Response Team. Kerberos is a networked authentication system which uses a trusted third party (a KDC) to authenticate clients and servers to each other. A double-free flaw was found in the krb5_recvauth() routine which may be triggered by a remote unauthenticated attacker. Although no exploit is currently known to exist, this issue could potentially be exploited to permit arbitrary code execution on a Key Distribution Center (KDC). The Common Vulnerabilities and Exposures project assigned the name CVE-2005-1689 to this issue. Daniel Wachdorf discovered a single byte heap overflow in the krb5_unparse_name() function, part of krb5-libs. Sucessful exploitation of this flaw would lead to a denial of service (crash). To trigger this flaw a possible hacker would need to have control of a kerberos realm that shares a cross-realm key with the target, making exploitation of this flaw unlikely. (CVE-2005-1175). The krb5-libs package contains libkrb5, which implements a majority of the Kerberos 5 APIs. The krb5_unparse_name() function may overflow a buffer by one byte if it is passed a properly formatted principal name structure. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1175 to this issue. The krb5_recvauth() function may corrupt its heap in certain error cases. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1689 to this issue. Gaël Delalleau discovered an information disclosure issue in the way some telnet clients handle messages from a server. A possible hacker could construct a malicious telnet server that collects information from the environment of any victim who connects to it using the Kerberos-aware telnet client (CVE-2005-0488). The rcp protocol permits a server to instruct a client to write to arbitrary files outside of the current directory. This could potentially cause a security issue if a user uses the Kerberos-aware rcp to copy files from a malicious server (CVE-2004-0175). All users of krb5 should update to these erratum packages which contain backported patches to correct these issues. Red Hat would like to thank the MIT Kerberos Development Team for their responsible disclosure of these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-562.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

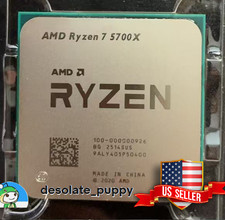
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
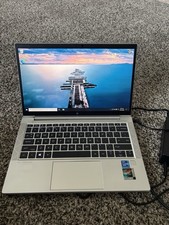
HP EliteBook 830 G8 Core I7-1185G7 3.00GHz Laptop 32GB RAM, 512GB SSD
$250.00
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
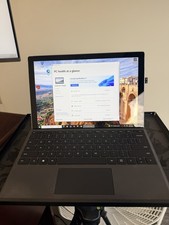
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
Apple Macbook Pro 13" M1 8-Core 16GB 512GB - Good
$464.99
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 9700X 8-Core 16-Thread 40MB Cache Socket AM5 9000 Series Processor
$245.99
Intel Core i7-11700T 1.4GHz Processor 8-Core Socket LGA1200 SRKNT
$129.95
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
|
||
|
No Discussions have been posted on this vulnerability. |