|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-527: openssh Vulnerability Assessment Details
|
RHSA-2005-527: openssh |
||
|
Check for the version of the openssh packages Detailed Explanation for this Vulnerability Assessment Updated openssh packages that fix a security issue, bugs, and add support for recording login user IDs for audit are now available for Red Hat Enterprise Linux 4. This update has been rated as having moderate security impact by the Red Hat Security Response Team. OpenSSH is OpenBSD's SSH (Secure SHell) protocol implementation. An error in the way OpenSSH handled GSSAPI credential delegation was discovered. OpenSSH as distributed with Red Hat Enterprise Linux 4 contains support for GSSAPI user authentication, typically used for supporting Kerberos. On OpenSSH installations which have GSSAPI enabled, this flaw could permit a user who sucessfully authenticates using a method other than GSSAPI to be delegated with GSSAPI credentials. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-2798 to this issue. Additionally, the following bugs have been addressed: The ssh command incorrectly failed when it was issued by the root user with a non-default group set. The sshd daemon could fail to properly close the client connection if multiple X clients were forwarded over the connection and the client session exited. The sshd daemon could bind only on the IPv6 address family for X forwarding if the port on IPv4 address family was already bound. The X forwarding did not work in such cases. This update also adds support for recording login user IDs for the auditing service. The user ID is attached to the audit records generated from the user's session. All users of openssh should upgrade to these updated packages, which contain backported patches to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-527.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

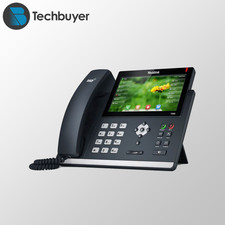
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
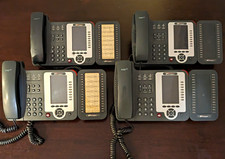
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
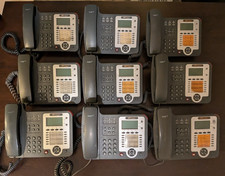
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
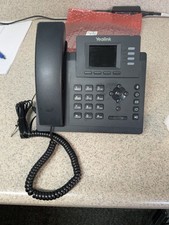
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
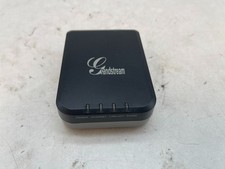
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
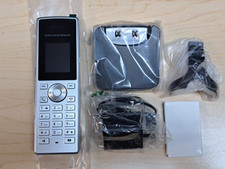
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28

Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
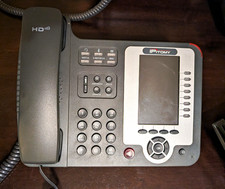
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
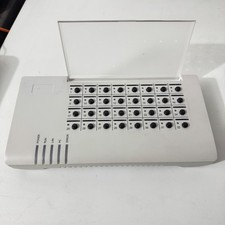
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |