|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-481: openssh Vulnerability Assessment Details
|
RHSA-2005-481: openssh |
||
|
Check for the version of the openssh packages Detailed Explanation for this Vulnerability Assessment Updated openssh packages that fix a potential security vulnerability and various other bugs are now available for Red Hat Enterprise Linux 2.1. This update has been rated as having low security impact by the Red Hat Security Response Team. OpenSSH is OpenBSD's SSH (Secure SHell) protocol implementation. SSH replaces rlogin and rsh, and provides secure encrypted communications between two untrusted hosts over an insecure network. X11 connections and arbitrary TCP/IP ports can also be forwarded over a secure channel. Public key authentication can be used for "passwordless" access to servers. The scp protocol permits a server to instruct a client to write to arbitrary files outside of the current directory. This could potentially cause a security issue if a user uses scp to copy files from a malicious server. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0175 to this issue. These updated packages also correct the following bug: On systems in which direct ssh access for the root user was disabled by configuration (setting "PermitRootLogin no"), attempts to guess the root password could be judged as sucessful or unsucessful by observing a delay. Users of openssh should upgrade to these updated packages, which contain backported patches to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-481.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

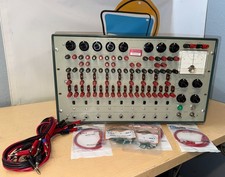
Refurbished Working 1960's Heathkit EC-1 Educational Electronic Analog Computer
$2999.99
Vintage George A Philbrick Researches Tube Analog Computer Module Serial 005503
$109.99
1969 EAI TR-20 Analog Computer Programming PACE Philbrick Electronic Associates
$36.00
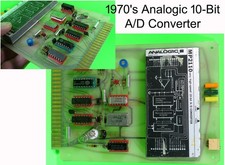
Vintage 1970’s Analogic MP2110 10-Bit A/D Converter Computer Circuit Board
$24.99
Extron RGB-160XI Analog Computer Video 60-378-01
$127.06
Vintage Goodyear Electronic GEDA Analog Computer Plug -- Extremely Rare
$179.00
VINTAGE 1970s SKIT Scientific Kit for Computer & Electronics SEALED INSIDE Rare
$380.00
Vintage Analog Computing Magazines For Atari Computer Owners No 11-20 Acceptable
$75.00
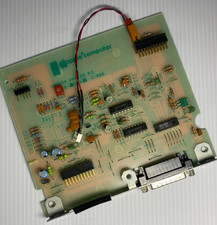
VINTAGE Apple Unidisk Analog Card - Circa 1986 | P/N 820-0190-A
$22.67
Vintage HP 82166A HP-IL Converter Custom “The BOX” TTL/DAC Interface Controller
$499.99
|
||
|
No Discussions have been posted on this vulnerability. |