|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-405: php Vulnerability Assessment Details
|
RHSA-2005-405: php |
||
|
Check for the version of the php packages Detailed Explanation for this Vulnerability Assessment Updated PHP packages that fix various security issues are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. PHP is an HTML-embedded scripting language commonly used with the Apache HTTP Web server. A bug was found in the way PHP processes IFF and JPEG images. It is possible to cause PHP to consume CPU resources for a short period of time by supplying a carefully crafted IFF or JPEG image. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2005-0524 and CVE-2005-0525 to these issues. A buffer overflow bug was also found in the way PHP processes EXIF image headers. It is possible for a possible hacker to construct an image file in such a way that it could execute arbitrary instructions when processed by PHP. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1042 to this issue. A denial of service bug was found in the way PHP processes EXIF image headers. It is possible for a possible hacker to cause PHP to enter an infinite loop for a short period of time by supplying a carefully crafted image file to PHP for processing. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1043 to this issue. Several bug fixes are also included in this update: - The security fixes in RHSA-2004-687 to the "unserializer" code introduced some performance issues. - In the gd extension, the "imagecopymerge" function did not correctly handle transparency. The original image was being obscured in the resultant image. - In the curl extension, safe mode was not enforced for 'file:///' URL lookups (CVE-2004-1392). Users of PHP should upgrade to these updated packages, which contain backported fixes for these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-405.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
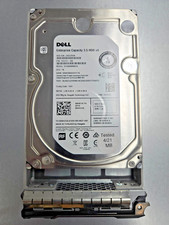
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
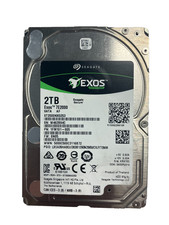
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
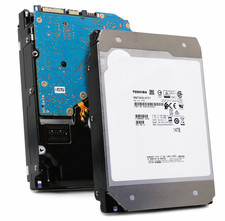
Toshiba 14TB MG07 MG07ACA14TEY 7.2K RPM SATA 6Gb/s 512e 3.5" Enterprise HDD
$339.00
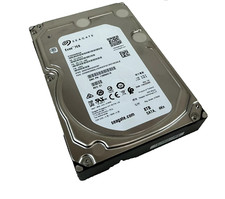
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99

Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
|
||
|
No Discussions have been posted on this vulnerability. |