|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-395: net Vulnerability Assessment Details
|
RHSA-2005-395: net |
||
|
Check for the version of the net packages Detailed Explanation for this Vulnerability Assessment Updated net-snmp packages that fix two security issues and various bugs are now available. This update has been rated as having low security impact by the Red Hat Security Response Team. SNMP (Simple Network Management Protocol) is a protocol used for network management. A denial of service bug was found in the way net-snmp uses network stream protocols. It is possible for a remote attacker to send a net-snmp agent a specially crafted packet that will crash the agent. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-2177 to this issue. An insecure temporary file usage bug was found in net-snmp's fixproc command. It is possible for a local user to modify the content of temporary files used by fixproc that can lead to arbitrary command execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-1740 to this issue. Additionally, the following bugs have been fixed: - The lmSensors are correctly recognized, snmp deamon no longer segfaults - The larger swap partition sizes are correctly reported - Querying hrSWInstalledLastUpdateTime no longer crashes the snmp deamon - Fixed error building ASN.1 representation - The 64-bit network counters correctly wrap - Large file systems are correctly handled - Snmptrapd initscript correctly reads options from its configuration file /etc/snmp/snmptrapd.options - Snmp deamon no longer crashes when restarted using the agentX protocol - snmp daemon now reports gigabit Ethernet speeds correctly - MAC adresses are shown when requested instead of IP adresses All users of net-snmp should upgrade to these updated packages, which resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-395.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

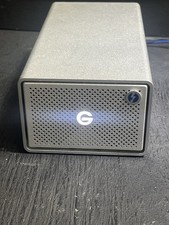
G-Technology G-RAID 24TB Dual-Drive External HDD TB3 USB 3.1 7200RPM Silver
$299.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
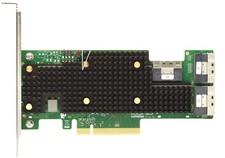
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
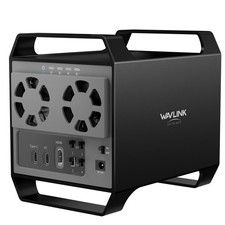
2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99
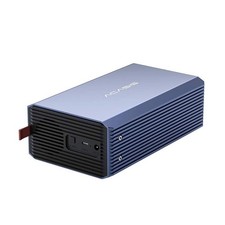
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
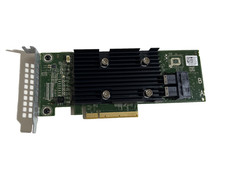
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
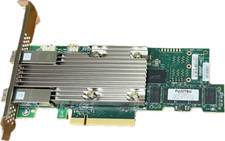
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |