|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-346: slocate Vulnerability Assessment Details
|
RHSA-2005-346: slocate |
||
|
Check for the version of the slocate packages Detailed Explanation for this Vulnerability Assessment An updated slocate package that fixes a denial of service and various bugs is available. This update has been rated as having low security impact by the Red Hat Security Response Team. Slocate is a security-enhanced version of locate. Like locate, slocate searches through a central database (updated nightly) for files that match a given pattern. Slocate permits you to quickly find files anywhere on your system. A bug was found in the way slocate scans the local filesystem. A carefully prepared directory structure could cause updatedb's file system scan to fail silently, resulting in an incomplete slocate database. The Common Vulnerabilities and Exposures project has assigned the name CVE-2005-2499 to this issue. Additionally this update addresses the following issues: - File system type exclusions were processed only when starting updatedb and did not reflect file systems mounted while updatedb was running (for example, automounted file systems.) - File system type exclusions were ignored for file systems that were mounted to a path containing a symbolic link. - Databases created by slocate were owned by the slocate group even if they were created by regular users. - The default configuration excluded /mnt/floppy, but not /media. - The default configuration did not exclude nfs4 file systems. Users of slocate are advised to upgrade to this updated package, which contains backported patches and is not affected by these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-346.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Vintage Intel 8085 CPU Processor Board Ceramic Gold IC Industrial Military Rare
$199.95
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
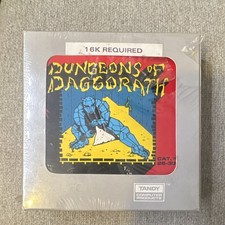
Dungeons of Daggorath TRS-80 Color Computer Tandy 26-3093 SEALED Vintage 1982
$119.99
vintage pentium 3 pc turns on no display no post
$150.00
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
New Old Stock Vintage Fujitsu Lifebook P1630 UMPC Laptop Retro Computer
$249.99
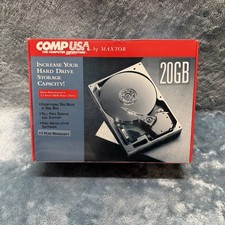
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
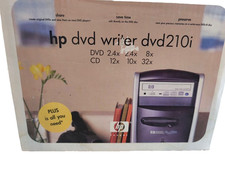
Vintage HP DVD Writer dvd210i Internal IDE Drive Q2116A BRAND NEW FACTORY SEALED
$58.85
|
||
|
No Discussions have been posted on this vulnerability. |