|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-331: XFree Vulnerability Assessment Details
|
RHSA-2005-331: XFree |
||
|
Check for the version of the XFree packages Detailed Explanation for this Vulnerability Assessment Updated XFree86 packages that fix a libXpm integer overflow flaw are now available. This update has been rated as having moderate security impact by the Red Hat Security Response Team. XFree86 is an open source implementation of the X Window System. It provides the basic low-level functionality that full-fledged graphical user interfaces (GUIs) such as GNOME and KDE are designed upon. An integer overflow flaw was found in libXpm, which is used by some applications for loading of XPM images. A possible hacker could create a malicious XPM file that would execute arbitrary code if opened by a victim using an application linked to the vulnerable library. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0605 to this issue. The updated XFree86 packages also address the following minor issues: - Updated XFree86-4.3.0-keyboard-disable-ioport-access-v3.patch to make warning messages less alarmist. - Backported XFree86-4.3.0-libX11-stack-overflow.patch from xorg-x11-6.8.1 packaging to fix stack overflow in libX11, which was discovered by new security features of gcc4. Users of XFree86 should upgrade to these updated packages, which contain a backported patch and are not vulnerable to this issue. Solution : http://rhn.redhat.com/errata/RHSA-2005-331.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

Genuine OEM Apple MagSafe 2 45W AC Adapter Charger for Macbook Air 2015 11" 13"
$14.24
OEM Apple Data Migration Toolkit for A1706 A1707 MacBook Pro PN 076-00236
$549.99
Genuine Apple Power Adapter Extension Cable 6FT White OEM MacBook MK122LL/A
$10.99
$6.99
OEM 45w T-Tip Power Adapter charger for Apple macbook air 2012-2017 A1436 A1466
$19.99
OEM Apple 45W A1436 Power Charger AC Adapter for MacBook Air MagSafe 2
$12.99
OEM 45W Charger For Apple MacBook Air 11-inch 13-inch Early 2012 2013 2014 2015
$26.98
Genuine Apple OEM A2164 30W USB-C AC Power Adapter with USB-C Cable, Very Good
$21.05
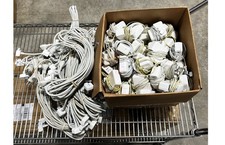
Lot of 100 OEM Apple Magsafe 2 45W AC Adapter A1436 with Power Cable - Grade D
$339.99
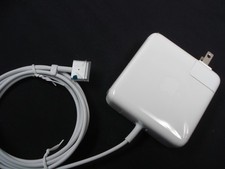
NEW Original OEM 60W Charger for 2012 2013 2014 2015 APPLE 13" MacBook Pro A1435
$25.95
|
||
|
No Discussions have been posted on this vulnerability. |