|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-327: telnet Vulnerability Assessment Details
|
RHSA-2005-327: telnet |
||
|
Check for the version of the telnet packages Detailed Explanation for this Vulnerability Assessment Updated telnet packages that fix two buffer overflow vulnerabilities are now available. This update has been rated as having important security impact by the Red Hat Security Response Team. The telnet package provides a command line telnet client. The telnet-server package includes a telnet daemon, telnetd, that supports remote login to the host machine. Two buffer overflow flaws were discovered in the way the telnet client handles messages from a server. A possible hacker may be able to execute arbitrary code on a victim's machine if the victim can be tricked into connecting to a malicious telnet server. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2005-0468 and CVE-2005-0469 to these issues. Additionally, the following bugs have been fixed in these erratum packages for Red Hat Enterprise Linux 2.1 and Red Hat Enterprise Linux 3: - telnetd could loop on an error in the child side process - There was a race condition in telnetd on a wtmp lock on some occasions - The command line in the process table was sometimes too long and caused bad output from the ps command - The 8-bit binary option was not working Users of telnet should upgrade to this updated package, which contains backported patches to correct these issues. Red Hat would like to thank iDEFENSE for their responsible disclosure of this issue. Solution : http://rhn.redhat.com/errata/RHSA-2005-327.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

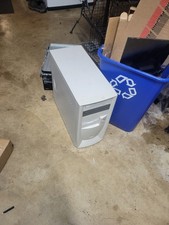
vintage pentium 3 pc turns on no display no post
$150.00
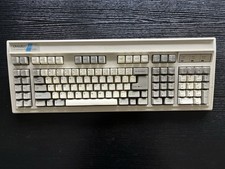
Vintage Computer Keyboard Northgate OMNIKEY Ultra
$120.00
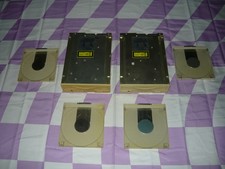
Lot of 2 Vintage Plextor PX-43CS SCSI CD-ROM Caddy Drives + 4 Caddies Used
$55.99
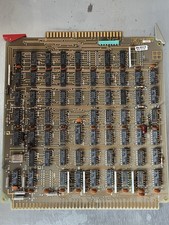
Vintage Hewlett Packard HP 13181-60074 Circuit Card Assembly / Interface Board.
$135.37
Vintage Avionics Gold CPU Board Intel MD8088 Ceramic LSI MCE Military Aerospace
$179.95
Vintage CREATIVE PC-DVD Dxr2 DVD2240E 1997
$59.00
Vintage Military Avionics PCB AlliedSignal 1750A CPU Ceramic Aerospace Board
$299.95
Original Vintage Old Style STANDARD Black CD Jewel Case (Heavy Duty) 90g Lot
$316.95
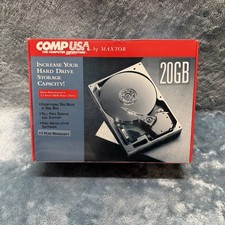
VINTAGE COLLECTIBLE Comp USA Maxtor 20 GB 3.5 Inch EIDE Hard Drive NEW SEALED
$500.00
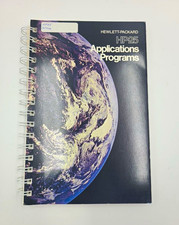
Vintage Hewlett-Packard HP-25 Applications Programs 1975 Manual 00025-90011
$29.50
|
||
|
No Discussions have been posted on this vulnerability. |