|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-325: kdelibs Vulnerability Assessment Details
|
RHSA-2005-325: kdelibs |
||
|
Check for the version of the kdelibs packages Detailed Explanation for this Vulnerability Assessment Updated kdelibs packages that fix several security issues are now available for Red Hat Enterprise Linux 4. This update has been rated as having important security impact by the Red Hat Security Response Team. The kdelibs package provides libraries for the K Desktop Environment. The International Domain Name (IDN) support in the Konqueror browser permited remote attackers to spoof domain names using punycode encoded domain names. Such domain names are decoded in URLs and SSL certificates in a way that uses homograph characters from other character sets, which facilitates phishing attacks. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0237 to this issue. Sebastian Krahmer discovered a flaw in dcopserver, the KDE Desktop Communication Protocol (DCOP) daemon. A local user could use this flaw to stall the DCOP authentication process, affecting any local desktop users and causing a reduction in their desktop functionality. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0396 to this issue. A flaw in the dcopidlng script was discovered. The dcopidlng script would create temporary files with predictable filenames which could permit local users to overwrite arbitrary files via a symlink attack. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0365 to this issue. Users of KDE should upgrade to these erratum packages which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-325.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

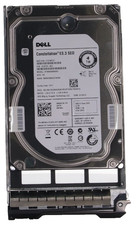
Dell 6P85J 4TB ST4000NM0063 7.2k 6Gb/s 3.5” SAS SED Hard Drive with Tray
$39.99
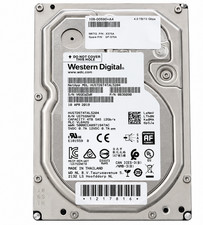
Western Digital HUS726T4TAL5204 4TB 7.2K SAS 12Gb/s 3.5" 512e HDD NetApp X375A
$64.00

Western Digital 1TB 3.5" SATA III 7200RPM Desktop Hard Drive
$34.99
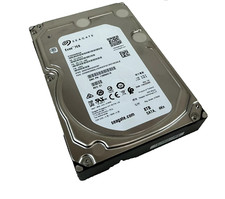
(ST8000NM0045) SEAGATE ENTERPRISE 8TB 7200RPM 4Kn SATA 6Gb/s 3.5" HARD DRIVE
$199.99
HGST 0F23072 Deskstar NAS 6TB SATA III 7200RPM 128MB 3.5in HDD
$84.99
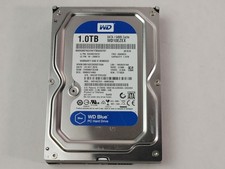
Western Digital WD Blue WD10EZEX 1 TB 3.5" SATA III Desktop Hard Drive
$23.99
Dell ST6000NM0034 1HT27Z-150 NWCCG 6TB SAS 3.5 7.2K ENTERPRISE SERVER DRIVE
$68.99
Seagate Exos ST2000NX0253 HDD 2TB SATA 7.2K 2.5" 512b/s
$55.00
DELL 2TB Enterprise HDD (7200RPM, 3.5", SATA III, 128MB Cache) HUS722T2TALA600
$49.95

Seagate ST12000NM0127 12TB 256MB 7200RPM 3.5" SATA 6.0Gb/s Enterprise Hard Drive
$318.99
|
||
|
No Discussions have been posted on this vulnerability. |