|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-294: kernel Vulnerability Assessment Details
|
RHSA-2005-294: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages are now available as part of ongoing support and maintenance of Red Hat Enterprise Linux version 3. This is the fifth regular update. The Linux kernel handles the basic functions of the operating system. This is the fifth regular kernel update to Red Hat Enterprise Linux 3. New features introduced by this update include: - support for 2-TB partitions on block devices - support for new disk, network, and USB devices - support for clustered APIC mode on AMD64 NUMA systems - netdump support on AMD64, Intel EM64T, Itanium, and ppc64 systems - diskdump support on sym53c8xx and SATA piix/promise adapters - NMI switch support on AMD64 and Intel EM64T systems There were many bug fixes in various parts of the kernel. The ongoing effort to resolve these problems has resulted in a marked improvement in the reliability and scalability of Red Hat Enterprise Linux 3. Some key areas affected by these fixes include the kernel's networking, SATA, TTY, and USB subsystems, as well as the architecture-dependent handling under the ia64, ppc64, and x86_64 directories. Scalability improvements were made primarily in the memory management and file system areas. A flaw in offset handling in the xattr file system code backported to Red Hat Enterprise Linux 3 was fixed. On 64-bit systems, a user who can access an ext3 extended-attribute-enabled file system could cause a denial of service (system crash). This issue is rated as having a moderate security impact (CVE-2005-0757). The following device drivers have been upgraded to new versions: 3c59x ------ LK1.1.18 3w-9xxx ---- 2.24.00.011fw (new in Update 5) 3w-xxxx ---- 1.02.00.037 8139too ---- (upstream 2.4.29) b44 -------- 0.95 cciss ------ v2.4.54.RH1 e100 ------- 3.3.6-k2 e1000 ------ 5.6.10.1-k2 lpfcdfc ---- 1.0.13 (new in Update 5) tg3 -------- 3.22RH Note: The kernel-unsupported package contains various drivers and modules that are unsupported and therefore might contain security problems that have not been addressed. All Red Hat Enterprise Linux 3 users are advised to upgrade their kernels to the packages associated with their machine architectures and configurations as listed in this erratum. Solution : http://rhn.redhat.com/errata/RHSA-2005-294.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

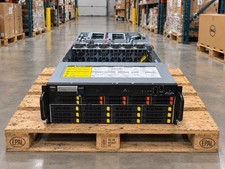
Gigabyte 4U AI Server 10x Nvidia GPU 2x Xeon Gold 6150 36 Core 2.7GHz DDR4 RAM
$1625.00

Dell EMC PowerEdge R440 Xeon silver 4215 2.5GHz 16 GB ram 2x 550W PSU No HDD
$275.00
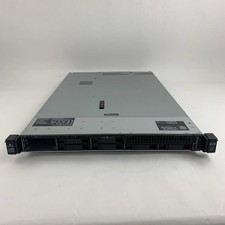
867959-B21 HPE ProLiant DL360 G10 CTO Server W/ 2x 865414-B21 1x 840140-001
$245.00

Dell PowerEdge R240 Intel Xeon E-2224 3.50GHz 8GB DDR4 ECC NO HDD 250W
$285.97

Dell PowerEdge R730XD 28 Core Server 2X Xeon E5-2680 V4 H730 32GB RAM No HDD
$378.93
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2690 v3 | 64gb Ram | 2x 1600W
$524.99
Dell PowerEdge C4130 1U AI GPU Server | 2x E5-2680 v3 | 32gb Ram | 2x 1600W
$409.99
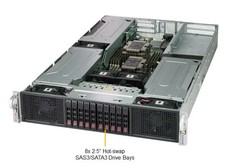
Supermicro 2U GPU Server SYS-2029GP-TR 2x Xeon 6130 32C 6x PCIe 3.0 x16 Slots
$745.00

Dell PowerEdge FX2s + 8x FC430 Blades 16x E5-2630v4 160 Cores Rails No PSU/RAM
$699.00

Dell PowerEdge R530 2x E5-2630v4 H330 iDRAC8 Port Card Riser No PSU/RAM/HDD
$99.99
|
||
|
No Discussions have been posted on this vulnerability. |