|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-106: openssh Vulnerability Assessment Details
|
RHSA-2005-106: openssh |
||
|
Check for the version of the openssh packages Detailed Explanation for this Vulnerability Assessment Updated openssh packages that fix a potential security vulnerability and various other bugs are now available for Red Hat Enterprise Linux 3. This update has been rated as having low security impact by the Red Hat Security Response Team. OpenSSH is OpenBSD's SSH (Secure SHell) protocol implementation. SSH replaces rlogin and rsh, and provides secure encrypted communications between two untrusted hosts over an insecure network. X11 connections and arbitrary TCP/IP ports can also be forwarded over a secure channel. Public key authentication can be used for "passwordless" access to servers. The scp protocol permits a server to instruct a client to write to arbitrary files outside of the current directory. This could potentially cause a security issue if a user uses scp to copy files from a malicious server. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0175 to this issue. These updated packages also correct the following bugs: On systems where direct ssh access for the root user was disabled by configuration (setting "PermitRootLogin no"), attempts to guess the root password could be judged as sucessful or unsucessful by observing a delay. On systems where the privilege separation feature was turned on, the user resource limits were not correctly set if the configuration specified to raise them above the defaults. It was also not possible to change an expired password. Users of openssh should upgrade to these updated packages, which contain backported patches to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-106.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

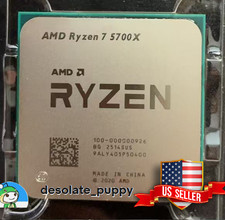
(New) AMD Ryzen 7 5700X 8 Core 16 Thread AM4 Unlocked 3.4 GHz CPU OEM Tray
$174.99
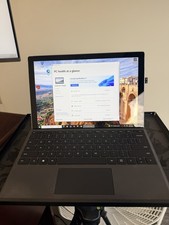
Microsoft Surface Pro 5 Silver 128GB SSD 4gb RAM
$97.97
SGIN 17.3" Laptop Intel Quad-Core Up to 2.4 GHZ 8GB RAM 256GB SSD HD
$229.99
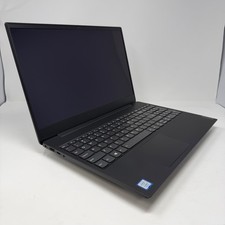
Lenovo IdeaPad S340-15IWL Laptop 15.6" Intel Core i3-8145U 8GB RAM 256GB SSD
$126.65
Intel Xeon E5 - 2667V2 / SR19W 3.30GHz 25MB 8-Core CPU Socket LGA2011
$30.00

AMD FX 8350 8-CORE 4.00GHz CPU FD8350FRW8KHK SOCKET AM3+ *QTY
$39.99
AMD Ryzen 7 5700G 8-Core 16-Thread 4.6GHz Max Boost, 3.8 GHz Base
$170.00
AMD Ryzen 7 9700X 8-Core 16-Thread 40MB Cache Socket AM5 9000 Series Processor
$245.99
Dell T7810 Workstation 8-Core 2.40GHz E5-2630 v3 No RAM GPU HDD OS
$259.98
Lenovo ThinkStation P520 Intel Xeon W-2245 8-Core 3.90GHz - NO RAM/ GPU/ HDD/ OS
$359.98
|
||
|
No Discussions have been posted on this vulnerability. |