|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-105: perl Vulnerability Assessment Details
|
RHSA-2005-105: perl |
||
|
Check for the version of the perl packages Detailed Explanation for this Vulnerability Assessment Updated Perl packages that fix several security issues are now available for Red Hat Enterprise Linux 3. Perl is a high-level programming language commonly used for system administration utilities and Web programming. Kevin Finisterre discovered a stack based buffer overflow flaw in sperl, the Perl setuid wrapper. A local user could create a sperl executable script with a carefully created path name, overflowing the buffer and leading to root privilege escalation. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0156 to this issue. Kevin Finisterre discovered a flaw in sperl which can cause debugging information to be logged to arbitrary files. By setting an environment variable, a local user could cause sperl to create, as root, files with arbitrary filenames, or append the debugging information to existing files. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0155 to this issue. Users of Perl are advised to upgrade to these updated packages, which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-105.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

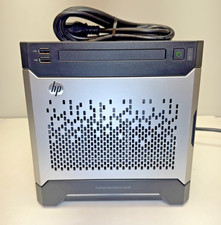
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
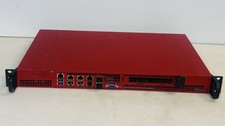
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
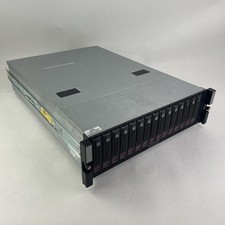
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
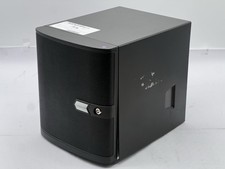
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro CSE-815-5 4B LFF Xeon E3-1245v6 16GB DDR4 1x 9361-8i 4x 1TB SATA HDD
$483.99
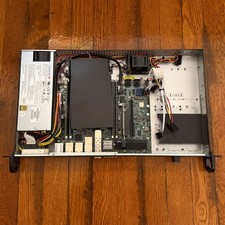
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |