|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-065: kdelibs Vulnerability Assessment Details
|
RHSA-2005-065: kdelibs |
||
|
Check for the version of the kdelibs packages Detailed Explanation for this Vulnerability Assessment Updated kdelibs packages that resolve security issues in Konqueror are now available for Red Hat Enterprise Linux 4. This update has been rated as having important security impact by the Red Hat Security Response Team. The kdelibs packages include libraries for the K Desktop Environment. Two flaws were found in the sandbox environment used to run Java-applets in the Konqueror web browser. If a user has Java enabled in Konqueror and visits a malicious website, the website could run a carefully crafted Java-applet and obtain escalated rights permiting reading and writing of arbitrary files with the rights of the victim. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-1145 to this issue. A flaw was discovered in the FTP kioslave. KDE applications such as Konqueror could be forced to execute arbitrary FTP commands via a carefully crafted ftp URL. The URL could also be crafted in such a way as to send an arbitrary email via SMTP. A possible hacker could make use of this flaw if a victim visits a malicious web site. The Common Vulnerabilities and Exposures project has assigned the name CVE-2004-1165 to this issue. Users should update to these erratum packages which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-065.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

RAM-HOL-SAM60CPU RAM USB-C Powered Dock for Samsung Tab Active5 - 3 - 2
$81.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung Chromebook 11.6" Intel Celeron Chrome OS Gray (Charger Inc)
$22.00
RAM-GDS-SKIN-SAM54-NG-1 RAM Mounts IntelliSkin® Next Gen for Samsung Tab Active4
$93.99
RAM-HOL-SAM52CPU RAM USB-C Powered Dock Samsung Tab Active4 Pro & Tab Active Pro
$81.99
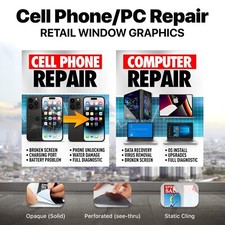
Cell Phone Smartphone Computer repair banner poster sign iphone Samsung
$89.99
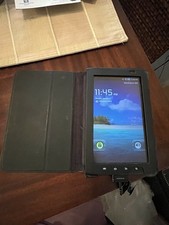
Samsung Galaxy Tab SCH-1800 7" 4GB Wi-Fi + Verizon Tablet Working
$30.00
Samsung Galaxy View Tablet 18.4 SM-T670/677A Charging Port 100% Original Oem
$98.99
Samsung Book Cover Keyboard Slim Black, Antimicrobial, English QWERTY EF-DT730
$55.00
|
||
|
No Discussions have been posted on this vulnerability. |