|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-061: squid Vulnerability Assessment Details
|
RHSA-2005-061: squid |
||
|
Check for the version of the squid packages Detailed Explanation for this Vulnerability Assessment An updated Squid package that fixes several security issues is now available. Squid is a full-featured Web proxy cache. A buffer overflow flaw was found in the Gopher relay parser. This bug could permit a remote Gopher server to crash the Squid proxy that reads data from it. Although Gopher servers are now quite rare, a malicious web page (for example) could redirect or contain a frame pointing to a possible hacker's malicious gopher server. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0094 to this issue. An integer overflow flaw was found in the WCCP message parser. It is possible to crash the Squid server if a possible hacker is able to send a malformed WCCP message with a spoofed source address matching Squid's "home router". The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0095 to this issue. A memory leak was found in the NTLM fakeauth_auth helper. It is possible that a possible hacker could place the Squid server under high load, causing the NTML fakeauth_auth helper to consume a large amount of memory, resulting in a denial of service. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0096 to this issue. Other security issues have been fixed too (see the advisory for full details) Users of Squid should upgrade to this updated package, which contains backported patches, and is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-061.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

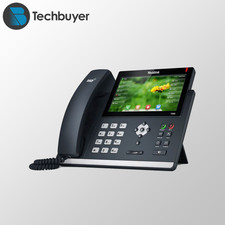
Yealink T48S VoIP/SIP Phone, 2 x Gigabit Ports PoE 7" Color SIP-T48S | TESTED
$34.95
Grandstream GXW4224 24-Line FXS Analog VoIP Gateway, Ethernet RJ-45 Black
$165.00
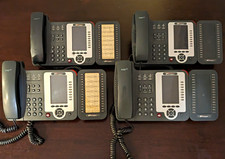
Lot of 4 USED IPitomy IP620-B with IPX-32 DSS Expansion Module VoIP Phone POE
$225.00
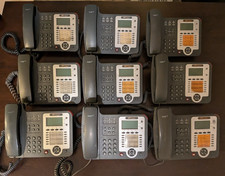
Lot of 9 Used IPitomy IP320-P HD POE Voice Speakerphone 12-Line VoIP Phone
$225.00
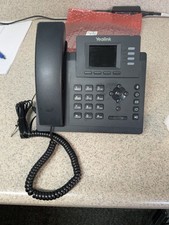
Yealink SIP-T33G IP Phone 4-LineSpeakerphone VoIP Desk Phone Black w/ Power Sply
$25.00
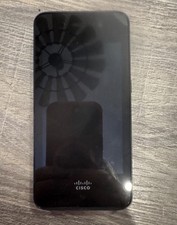
NEW Cisco CP-840 Wireless WiFi IP VoIP Phone 840 w Battery Charger Cable
$800.00
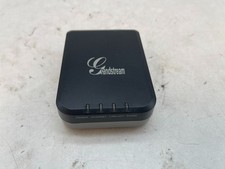
Grandstream HT701 1-Port FXS Analog Telephone Adapter ATA VoIP Gateway -Free S/H
$19.99
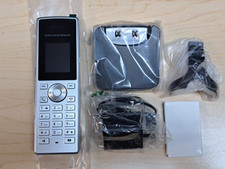
Grandstream WP810 Portable Cordless Wi-Fi IP Phone
$49.28
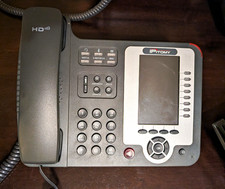
Set of 5 USED IPitomy IP620-B HD VoIP 6-Line IP Phone Speakerphone Ethernet POE
$149.00
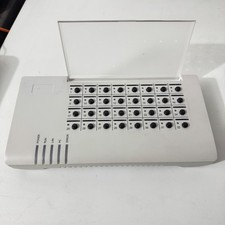
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |