|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-034: xpdf Vulnerability Assessment Details
|
RHSA-2005-034: xpdf |
||
|
Check for the version of the xpdf packages Detailed Explanation for this Vulnerability Assessment An updated xpdf package that fixes several security issues is now available. This update has been rated as having important security impact by the Red Hat Security Response Team. Xpdf is an X Window System based viewer for Portable Document Format (PDF) files. A buffer overflow flaw was found in the Gfx::doImage function of Xpdf. An attacker could construct a carefully crafted PDF file that could cause Xpdf to crash or possibly execute arbitrary code when opened. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-1125 to this issue. A buffer overflow flaw was found in the Decrypt::makeFileKey2 function of Xpdf. A possible hacker could construct a carefully crafted PDF file that could cause Xpdf to crash or possibly execute arbitrary code when opened. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0064 to this issue. During a source code audit, Chris Evans and others discovered a number of integer overflow bugs that affected all versions of Xpdf. A possible hacker could construct a carefully crafted PDF file that could cause Xpdf to crash or possibly execute arbitrary code when opened. This issue was assigned the name CVE-2004-0888 by The Common Vulnerabilities and Exposures project (cve.mitre.org). Red Hat Enterprise Linux 4 contained a fix for this issue, but it was found to be incomplete and left 64-bit architectures vulnerable. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0206 to this issue. All users of Xpdf should upgrade to this updated package, which contains backported patches to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-034.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

SFP TO RJ45 TRANSCEIVER SFP MODULE COPPER SFP OPTICAL PORT TO RJ45 ETHERNET PORT
$7.99
Dell Intel X710-DA2 5N7Y5 Dual-Port 10GbE SFP+ PCIe 3.0 x8 Network Adapter
$27.50
Cisco Acacia DP04QSDD-E25-840 400G QSFP-DD Coherent DCO Transceiver Module
$699.99

Cisco QSFP-40G-SR-BD Module 10-2945-02 NEW CLAMSHELL
$45.50

Genuine Cisco SFP-10G-SR 0-2415-03 10 Gigabit Transceiver
$5.40
Lot of 5 Cisco 10G SFP+ 850nm 300m Transceiver Module P/N: SFP-10G-SR-10-2415-03
$15.00
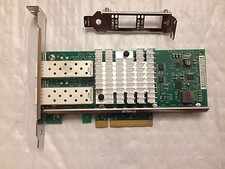
Intel X520-DA2 10Gb 10Gbe 10 Gigabit Network Adapter NIC Dual Port E10G42BTDA
$28.94
HP 560SFP+ 10GB 2-port PCIe NIC Ethernet ADAPTER 669279-001 w/ (2) 10GB SFP+
$16.99
NEW Sealed Cisco SFP-10G-LR 10GBASE-LR SFP+ 1310nm 10km *US Shipping*
$24.00
Dell 10 Gigabit SFP+ SR Transceiver 0XYD50 NEW SEALED
$24.99
|
||
|
No Discussions have been posted on this vulnerability. |