|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2005-025: exim Vulnerability Assessment Details
|
RHSA-2005-025: exim |
||
|
Check for the version of the exim packages Detailed Explanation for this Vulnerability Assessment Updated exim packages that resolve security issues are now available for Red Hat Enterprise Linux 4. This update has been rated as having moderate security impact by the Red Hat Security Response Team. Exim is a mail transport agent (MTA) developed at the University of Cambridge for use on Unix systems connected to the Internet. A buffer overflow was discovered in the spa_base64_to_bits function in Exim, as originally obtained from Samba code. If SPA authentication is enabled, a remote attacker may be able to exploit this vulnerability to execute arbitrary code as the 'exim' user. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0022 to this issue. Please note that SPA authentication is not enabled by default in Red Hat Enterprise Linux 4. Buffer overflow flaws were discovered in the host_aton and dns_build_reverse functions in Exim. A local user can trigger these flaws by executing exim with carefully crafted command line arguments and may be able to gain the rights of the 'exim' account. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2005-0021 to this issue. Users of Exim are advised to update to these erratum packages which contain backported patches to correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2005-025.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |

2-Bay/4-Bay Hard Drive Enclosure for 3.5"/2.5'' SATA HDD/SSD 10Gbps USB-C 3.2
$75.99

OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
Broadcom 9600-24i RAID Controller PCIe Gen 4.1 Tri-Mode NEW 05-50111-01004
$649.99
Intel VROC Premium RAID Controller Card PCIe Add-On Module VROCPREMMOD
$265.00
Acasis USB 3.2 2 Bay HDD RAID Enclosure for 2.5/3.5" SATA Drives External Array
$55.00
MegaRAID 9580-8i8e 16-port 12G SAS/SATA/NVMe 8GB PCIe RAID - 05-50076-00
$1619.19
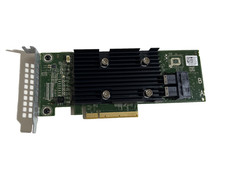
Dell PowerEdge HBA330 LP PCI-E 12GBs RAID SAS Controller Adapter J7TNV
$18.95
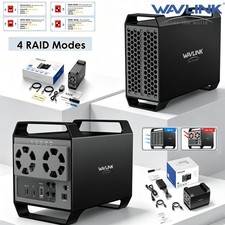
WAVLINK RAID 2 Bay Hard Drive Docking Station SATA 2.5/3.5'' SSD HDD Enclosure
$119.99
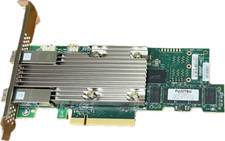
Broadcom MegaRAID 9480-8e Fujitsu PRAID EP540e SAS RAID Card (Replac 9380-8e) 8i
$228.00
Intel® Integrated RAID Mezzanine Module RMS3HC080 SAS/SATA H24093-204
$24.97
|
||
|
No Discussions have been posted on this vulnerability. |