|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-611: mysql Vulnerability Assessment Details
|
RHSA-2004-611: mysql |
||
|
Check for the version of the mysql packages Detailed Explanation for this Vulnerability Assessment An updated mysql-server package that fixes various security issues is now available in the Red Hat Enterprise Linux 3 Extras channel of Red Hat Network. MySQL is a multi-user, multi-threaded SQL database server. A number of security issues that affect the mysql-server package have been reported. Although Red Hat Enterprise Linux 3 does not ship with the mysql-server package, the affected package is available from the Red Hat Network Extras channel. Oleksandr Byelkin discovered that "ALTER TABLE ... RENAME" checked the CREATE/INSERT rights of the old table instead of the new one. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0835 to this issue. Lukasz Wojtow discovered a buffer overrun in the mysql_real_connect function. In order to exploit this issue a possible hacker would need to force the use of a malicious DNS server (CVE-2004-0836). Dean Ellis discovered that multiple threads ALTERing the same (or different) MERGE tables to change the UNION could cause the server to crash or stall (CVE-2004-0837). Sergei Golubchik discovered that if a user is granted rights to a database with a name containing an underscore ("_"), the user also gains the ability to grant rights to other databases with similar names (CVE-2004-0957). Users of mysql-server should upgrade to these erratum packages, which correct these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-611.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

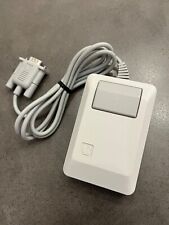
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$49.99
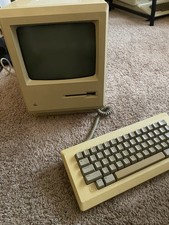
Apple Macintosh 128k Desktop computer. Upgraded to 512k
$300.00
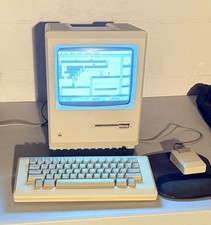
1984 APPLE MACINTOSH 128K MATCHING # BOX Set Original Mac Model M0001 WORKS RARE
$6299.00

1984 APPLE MACINTOSH 128K FIRST MAC Model M0001 PICASSO KIT Discs Harvard Rare
$1800.00
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$59.99
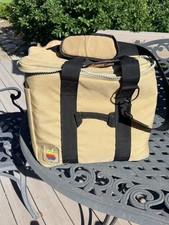
Vintage Apple Macintosh 128K 512K Carrying Case Rainbow Logo Excellent Cond
$140.00
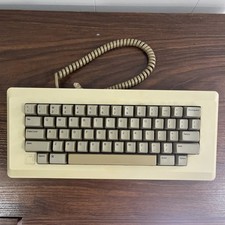
Apple Keyboard and Cable for Macintosh 128k 512k Mac Plus RARE Vintage M0110
$129.99
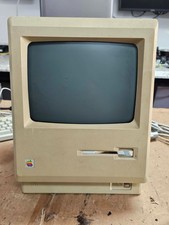
Vintage Early Week 12 1984 Apple Macintosh 128K Computer M0001 w/Analog Board+
$209.99
Apple Keyboard for Macintosh 128k 512k Mac Plus RARE Vintage M0110 (010)
$149.00
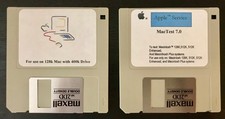
Apple Macintosh Mac 128k - 512k Boot / Diagnostics 2 Disk Set for Classic Macs
$14.99
|
||
|
No Discussions have been posted on this vulnerability. |