|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-486: galeon Vulnerability Assessment Details
|
RHSA-2004-486: galeon |
||
|
Check for the version of the galeon packages Detailed Explanation for this Vulnerability Assessment Updated mozilla packages that fix a number of security issues are now available. Mozilla is an open source Web browser, advanced email and newsgroup client, IRC chat client, and HTML editor. Jesse Ruderman discovered a cross-domain scripting bug in Mozilla. If a user is tricked into dragging a javascript link into another frame or page, it becomes possible for a possible hacker to steal or modify sensitive information from that site. Additionally, if a user is tricked into dragging two links in sequence to another window (not frame), it is possible for the attacker to execute arbitrary commands. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0905 to this issue. Gael Delalleau discovered an integer overflow which affects the BMP handling code inside Mozilla. A possible hacker could create a carefully crafted BMP file in such a way that it would cause Mozilla to crash or execute arbitrary code when the image is viewed. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0904 to this issue. Georgi Guninski discovered a stack-based buffer overflow in the vCard display routines. A possible hacker could create a carefully crafted vCard file in such a way that it would cause Mozilla to crash or execute arbitrary code when viewed. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0903 to this issue. Wladimir Palant discovered a flaw in the way javascript interacts with the clipboard. It is possible that a possible hacker could use malicious javascript code to steal sensitive data which has been copied into the clipboard. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0908 to this issue. Georgi Guninski discovered a heap based buffer overflow in the "Send Page" feature. It is possible that a possible hacker could construct a link in such a way that a user attempting to forward it could result in a crash or arbitrary code execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0902 to this issue. Users of Mozilla should update to these updated packages, which contain backported patches and are not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-486.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

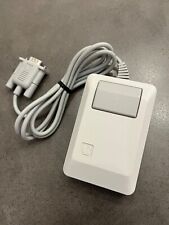
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$49.99
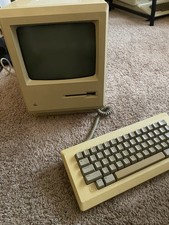
Apple Macintosh 128k Desktop computer. Upgraded to 512k
$300.00
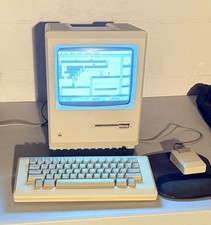
1984 APPLE MACINTOSH 128K MATCHING # BOX Set Original Mac Model M0001 WORKS RARE
$6299.00

1984 APPLE MACINTOSH 128K FIRST MAC Model M0001 PICASSO KIT Discs Harvard Rare
$1800.00
Macintosh Platinum Mouse - Apple 128K 512K 512Ke Mac Plus Lisa IIe M0100 - NEW
$59.99
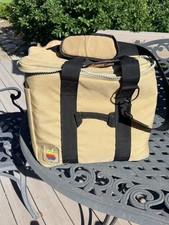
Vintage Apple Macintosh 128K 512K Carrying Case Rainbow Logo Excellent Cond
$140.00
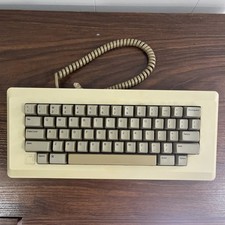
Apple Keyboard and Cable for Macintosh 128k 512k Mac Plus RARE Vintage M0110
$129.99
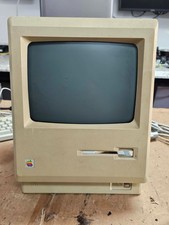
Vintage Early Week 12 1984 Apple Macintosh 128K Computer M0001 w/Analog Board+
$209.99
Apple Keyboard for Macintosh 128k 512k Mac Plus RARE Vintage M0110 (010)
$149.00
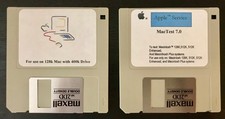
Apple Macintosh Mac 128k - 512k Boot / Diagnostics 2 Disk Set for Classic Macs
$14.99
|
||
|
No Discussions have been posted on this vulnerability. |