|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-413: kernel Vulnerability Assessment Details
|
RHSA-2004-413: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages that fix several security issues in Red Hat Enterprise Linux 3 are now available. The Linux kernel handles the basic functions of the operating system. Paul Starzetz discovered flaws in the Linux kernel when handling file offset pointers. These consist of invalid conversions of 64 to 32-bit file offset pointers and possible race conditions. A local unprivileged user could make use of these flaws to access large portions of kernel memory. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0415 to this issue. These packages contain a patch written by Al Viro to correct these flaws. Red Hat would like to thank iSEC Security Research for disclosing this issue and a number of vendor-sec participants for reviewing and working on the patch to this issue. In addition, these packages correct a number of minor security issues: An bug in the e1000 network driver. This bug could be used by local users to leak small amounts of kernel memory (CVE-2004-0535). A bug in the SoundBlaster 16 code which does not properly handle certain sample sizes. This flaw could be used by local users to crash a system (CVE-2004-0178). A possible NULL-pointer dereference in the Linux kernel prior to 2.4.26 on the Itanium platform could permit a local user to crash a system (CVE-2004-0447). Inappropriate permissions on /proc/scsi/qla2300/HbaApiNode (CVE-2004-0587). All Red Hat Enterprise Linux 3 users are advised to upgrade their kernels to the packages associated with their machine architectures and configurations as listed in this erratum. Solution : http://rhn.redhat.com/errata/RHSA-2004-413.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

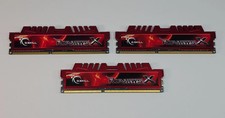
16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
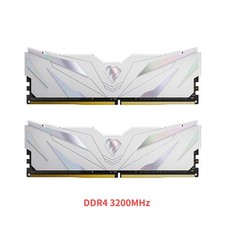
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
Samsung M391A1K43BB2-CTDQ 4 x 8GB 1Rx8 PC4-2666V DDR4 UDIMM RAM Memory
$140.00
Lot of 5 DDR4 Mixed Desktop RAM 28GB Total G.Skill Patriot Ballistix XPG Tested
$358.50
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
Crucial 32GB(4 x 8GB) CT8G4DFS824A.C8FDD1 DDR4-2400 UDIMM Desktop RAM - CR352A
$89.95
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
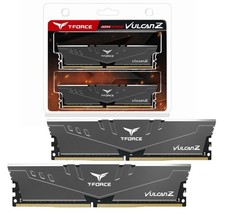
TeamGroup T-FORCE VULCAN Z 16GB (2 x 8GB) DDR4 3000Mz (PC4 24000) Desktop Memory
$188.00
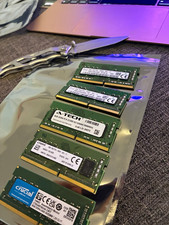
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |