|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-400: gaim Vulnerability Assessment Details
|
RHSA-2004-400: gaim |
||
|
Check for the version of the gaim packages Detailed Explanation for this Vulnerability Assessment An updated gaim package that fixes several security issues is now available. Gaim is an instant messenger client that can handle multiple protocols. Buffer overflow bugs were found in the Gaim MSN protocol handler. In order to exploit these bugs, a possible hacker would have to perform a man in the middle attack between the MSN server and the vulnerable Gaim client. Such an attack could permit arbitrary code execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0500 to this issue. Buffer overflow bugs have been found in the Gaim URL decoder, local hostname resolver, and the RTF message parser. It is possible that a remote attacker could send carefully crafted data to a vulnerable client and lead to a crash or arbitrary code execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0785 to this issue. A shell escape bug has been found in the Gaim smiley theme file installation. When a user installs a smiley theme, which is contained within a tar file, the unarchiving of the data is done in an unsafe manner. A possible hacker could create a malicious smiley theme that would execute arbitrary commands if the theme was installed by the victim. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0784 to this issue. An integer overflow bug has been found in the Gaim Groupware message receiver. It is possible that if a user connects to a malicious server, a possible hacker could send carefully crafted data which could lead to arbitrary code execution on the victims machine. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0754 to this issue. Users of Gaim are advised to upgrade to this updated package which contains Gaim version 0.82 and is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-400.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
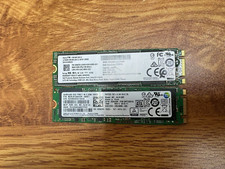
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
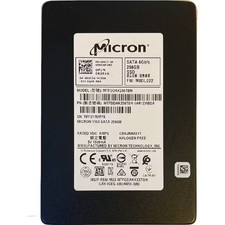
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
|
||
|
No Discussions have been posted on this vulnerability. |