|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-378: ethereal Vulnerability Assessment Details
|
RHSA-2004-378: ethereal |
||
|
Check for the version of the ethereal packages Detailed Explanation for this Vulnerability Assessment Updated Ethereal packages that fix various security vulnerabilities are now available. Ethereal is a program for monitoring network traffic. The SNMP dissector in Ethereal releases 0.8.15 through 0.10.4 contained a memory read flaw. On a system where Ethereal is running, a remote attacker could send malicious packets that could cause Ethereal to crash or possibly execute arbitrary code. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0635 to this issue. The SMB dissector in Ethereal releases 0.9.15 through 0.10.4 contained a null pointer flaw. On a system where Ethereal is running, a remote attacker could send malicious packets that could cause Ethereal to crash. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0634 to this issue. The iSNS dissector in Ethereal releases 0.10.3 through 0.10.4 contained an integer overflow flaw. On a system where Ethereal is running, a remote attacker could send malicious packets that could cause Ethereal to crash or possibly execute arbitrary code. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0633 to this issue. Users of Ethereal should upgrade to these updated packages, which contain a version that is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-378.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

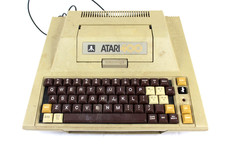
VTG Atari 400 Home Computer System ** Sold "AS-IS" for Parts or Repair
$88.75
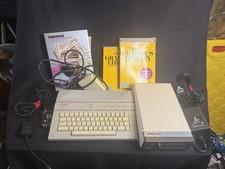
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
DEFECTIVE Atari 810 Vintage Computer Disk Drive powers on Unit Only Boo G3D
$49.29
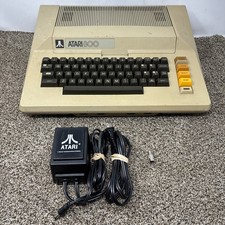
Atari 800 8-bit Computer System Fully Tested Great Condition 48k READ
$350.00
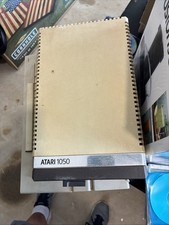
Atari 1050 Floppy Disk Drive with Power Supply, MPN C061636 (Vintage)
$80.00
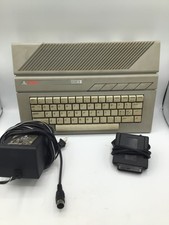
Atari XE 130XE Computer NTSC with Power Supply Powers On Untested
$159.95
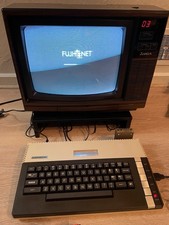
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
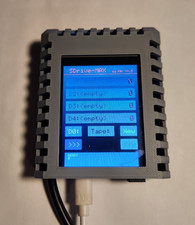
SDrive Max Floppy Drive Emulator Atari 8-Bit 400/800/XL/XE Firmware 1.5 USB C R2
$70.00
UNOCART-2600 SD card Multi Rom Cartridge for ATARI 2600 with CASE
$34.25
Vintage Atari SF354 Floppy Disk Drive & Power Supply FOR PARTS OR REPAIR AS IS
$120.00
|
||
|
No Discussions have been posted on this vulnerability. |