|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-323: lha Vulnerability Assessment Details
|
RHSA-2004-323: lha |
||
|
Check for the version of the lha packages Detailed Explanation for this Vulnerability Assessment An updated lha package that fixes a buffer overflow is now available. LHA is an archiving and compression utility for LHarc format archives. Lukasz Wojtow discovered a stack-based buffer overflow in all versions of lha up to and including version 1.14. A carefully created archive could permit a possible hacker to execute arbitrary code when a victim extracts or tests the archive. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0769 to this issue. Buffer overflows were discovered in the command line processing of all versions of lha up to and including version 1.14. If a malicious user could trick a victim into passing a specially crafted command line to the lha command, it is possible that arbitrary code could be executed. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2004-0771 and CVE-2004-0694 to these issues. Thomas Biege discovered a shell meta character command execution vulnerability in all versions of lha up to and including 1.14. A possible hacker could create a directory with shell meta characters in its name which could lead to arbitrary command execution. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0745 to this issue. Users of lha should update to this updated package which contains backported patches and is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-323.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

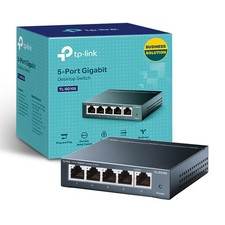
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$19.99
Cisco Catalyst 2960-48TT-L 48-Port Fast Ethernet Managed Rackmount Switch
$46.99
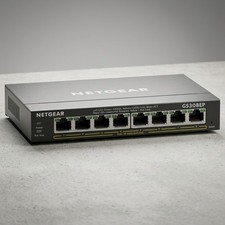
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$49.99
TP-Link TL-SG1048 48-Port Gigabit Rackmount Switch New Factory Sealed
$199.99
5 Port Gigabit Unmanaged Ethernet Switch, Home Network Hub, Office Ethernet S...
$9.64
10-Port Gigabit PoE Network Switch with 8 PoE+ Ports with 2 Combo SFP Slots 125W
$39.99
TP-Link TL-SG105, 5 Port Gigabit Unmanaged Ethernet Switch, Network Hub, Ethern
$15.25
Arista DCS-7010T-48-R 48P 1GbE 4P 10GbE SFP+ RA Switch with rack mounts
$69.00
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$25.99
Cisco WS-C3650-12X48UR-L 48-Port Stackable Layer 3 8x10G SFP+ Port Switch
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |