|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-153: cvs Vulnerability Assessment Details
|
RHSA-2004-153: cvs |
||
|
Check for the version of the cvs packages Detailed Explanation for this Vulnerability Assessment Updated cvs packages that fix a client vulnerability that could be exploited by a malicious server are now available. [Updated Apr 19 2004] The description text has been updated to include CVE-2004-0405 which was also fixed but not mentioned when this advisory was first released. There has been no change to the packages associated with this advisory. CVS is a version control system frequently used to manage source code repositories. Sebastian Krahmer discovered a flaw in CVS clients where rcs diff files can create files with absolute pathnames. A possible hacker could create a fake malicious CVS server that would cause arbitrary files to be created or overwritten when a victim connects to it. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0180 to this issue. Derek Price discovered a vulnerability whereby a CVS pserver could be abused by a malicious client to view the contents of certain files outside of the CVS root directory using relative pathnames containing "../". The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2004-0405 to this issue. Users of CVS are advised to upgrade to these erratum packages, which contain a patch correcting this issue. Solution : http://rhn.redhat.com/errata/RHSA-2004-153.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

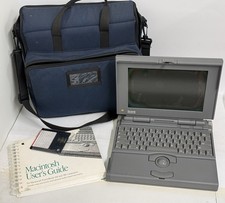
READ - UNTESTED Apple Macintosh PowerBook 160 M4550 Vintage Laptop
$299.00
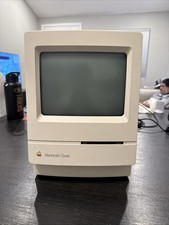
Apple Macintosh Classic M1420 Vintage Desktop Computer Model Macintosh Classic
$100.00
READ - Vintage Apple Macintosh SE/30 - Boots
$850.00
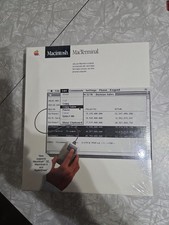
Macintosh MacTerminal M0521 Version 1.0. Vintage Apple software 1984 Sealed
$129.99
Vintage 1983 Apple II ProDOS User's Kit Computer Software NEW SEALED A2D2010
$64.95
Apple Computer cards VTG 670-8020-B 607-0103-C 607-0291-C AST -Orange Micro ++
$169.00
Vintage Apple II Avant-Garde Creations Super Shape Draw And Animate 1981
$295.00
Vintage Apple iBook G3 12.1” 500MHz 2001 Restored, SSD Upgraded Mac OS 9.2/OS X
$180.00
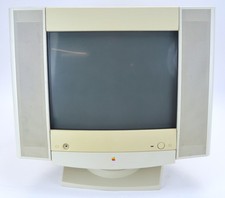
Vintage Apple Multiple Scan 15av Display Monitor M4681
$299.99
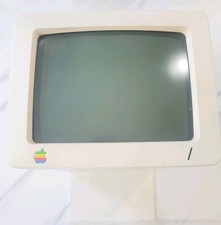
Vintage Apple Monitor IIc 9" Green Monochrome 06/1985 A2M4090 October 1984 Stand
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |