|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2004-002: ethereal Vulnerability Assessment Details
|
RHSA-2004-002: ethereal |
||
|
Check for the version of the ethereal packages Detailed Explanation for this Vulnerability Assessment Updated Ethereal packages that fix two security vulnerabilities are now available. Ethereal is a program for monitoring network traffic. Two security issues have been found that affect Ethereal. By exploiting these issues it may be possible to make Ethereal crash by injecting an intentionally malformed packet onto the wire or by convincing someone to read a malformed packet trace file. It is not known if these issues could permit arbitrary code execution. The SMB dissector in Ethereal before 0.10.0 permits remote attackers to cause a denial of service via a malformed SMB packet that triggers a segmentation fault during processing of Selected packets. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-1012 to this issue. The Q.931 dissector in Ethereal before 0.10.0 permits remote attackers to cause a denial of service (crash) via a malformed Q.931, which triggers a null dereference. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-1013 to this issue. Users of Ethereal should update to these erratum packages containing Ethereal version 0.10.0, which is not vulnerable to these issues. Solution : http://rhn.redhat.com/errata/RHSA-2004-002.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

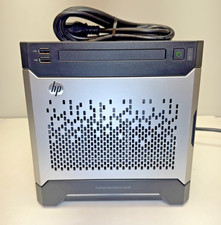
HP ProLiant MicroServer Gen8 G1610T @2.3 GHz, 16GB, 712317-001 NO HDD/OS
$199.00
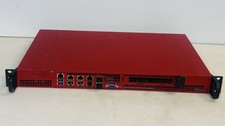
Supermicro 1U Network Server Appliance 16GB RAM 800GB SSD 6 LAN Ports Powers On
$450.00
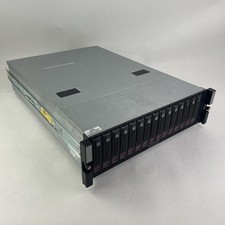
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
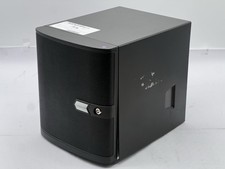
Nasuni NF-50 Supermicro Server, Atom CPU C2558, @ 2.40GHz, 8GB RAM-No HDD/OS/AC
$250.00
New Barebones Supermicro 5019D Server, 4C/8T Xeon D-2123T, 1U Rackmountable, 10G
$449.99
Supermicro 2U X10DRU-i 2x E5-2680 v3 2.5ghz 32gb Ram 240gb SSD 2x GPU *READ*
$369.99
Supermicro 5019D-4C-FN8TP Xeon D-2123IT (4C/8T) 64GB DDR4 10GbE 480GB 1U Server
$689.00
Supermicro 1027GR-TSF 1U Rackmount Server 2x Xeon 2.3GHz 128GB DDR3
$219.99
$280.00
Supermicro CSE-937 3U Storage Chassis No CPU No HDD No Ram Tested & Reset
$129.99
|
||
|
No Discussions have been posted on this vulnerability. |