|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-360: apache Vulnerability Assessment Details
|
RHSA-2003-360: apache |
||
|
Check for the version of the apache packages Detailed Explanation for this Vulnerability Assessment Updated Apache packages that fix a minor security issue are now available for Red Hat Enterprise Linux. The Apache HTTP server is a powerful, full-featured, efficient, and freely-available Web server. An issue in the handling of regular expressions from configuration files was discovered in releases of the Apache HTTP Server version 1.3 prior to 1.3.29. To exploit this issue a possible hacker would need to have the ability to write to Apache configuration files such as .htaccess or httpd.conf. A carefully-crafted configuration file can cause an exploitable buffer overflow and would permit the attacker to execute arbitrary code in the context of the server (in default configurations as the 'apache' user). The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0542 to this issue. This update also includes an alternative version of the httpd binary which supports setting the MaxClients configuration directive to values above 256. All users of the Apache HTTP Web Server are advised to upgrade to the applicable errata packages, which contain back-ported fixes correcting the above security issue. Note that the instructions in the "Solution" section of this errata contain additional steps required to complete the upgrade process. Solution : http://rhn.redhat.com/errata/RHSA-2003-360.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |


Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$379.00

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$60.00
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99

Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
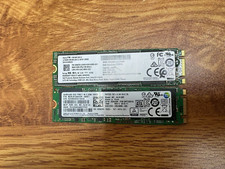
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
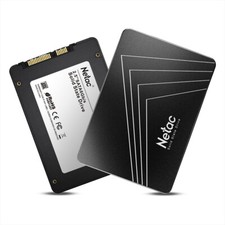
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 256GB SSD 2.5'' SATA III 6Gb/s Internal Solid State Drive 500MB/s PC/Latop
$40.00
|
||
|
No Discussions have been posted on this vulnerability. |