|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-293: openssl Vulnerability Assessment Details
|
RHSA-2003-293: openssl |
||
|
Check for the version of the openssl packages Detailed Explanation for this Vulnerability Assessment Updated OpenSSL packages are available that fix ASN.1 parsing vulnerabilities. OpenSSL is a commercial-grade, full-featured, and open source toolkit that implements Secure Sockets Layer (SSL v2/v3) and Transport Layer Security (TLS v1) protocols as well as a full-strength general purpose cryptography library. NISCC testing of implementations of the SSL protocol uncovered two bugs in OpenSSL 0.9.6. The parsing of unusual ASN.1 tag values can cause OpenSSL to crash. A remote attacker could trigger this bug by sending a carefully crafted SSL client certificate to an application. The effects of such an attack vary depending on the application targetted against Apache the effects are limited, as the attack would only cause child processes to die and be replaced. An attack against other applications that use OpenSSL could result in a Denial of Service. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2003-0543 and CVE-2003-0544 to this issue. These erratum packages contain a patch provided by the OpenSSL group that protects against this issue. Because server applications are affected by this issue, users are advised to either restart all services that use OpenSSL functionality or reboot their systems after installing these updates. Red Hat would like to thank NISCC and Stephen Henson for their work on this vulnerability. These packages also include a patch from OpenSSL 0.9.6f which removes the calls to abort the process in certain circumstances. Red Hat would like to thank Patrik Hornik for notifying us of this issue. Solution : http://rhn.redhat.com/errata/RHSA-2003-293.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

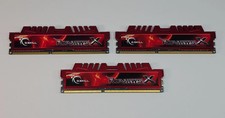
16GB KIT (2x8GB) DDR3 Gamer Desktop RAM PC3 MIXED BRANDS VIPER VENGEANCE FURY
$10.00
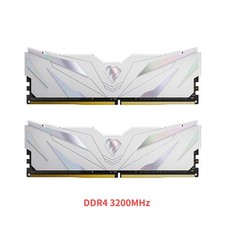
Netac DDR4 32GB 16GB DDR4 3200MHz UDIMM C16 Desktop Internal Memory RAM Kit
$99.99

Samsung 32GB DDR4-2666 PC4-21300 288-Pin DIMM RAM M393A4K40CB1CRC0Q
$185.00
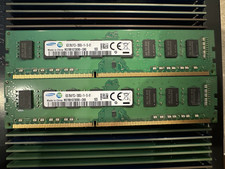
Major Brand 16GB (2x8GB) PC3-12800U DDR3-1600MHz DDR3-12800 DESKTOP RAM NON-ECC
$29.99
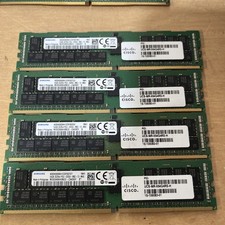
Samsung 64GB PC4-2666V-R 2S2Rx4 DDR4 ECC REG RDIMM - M393A8K40B22-CWD6Y
$270.00
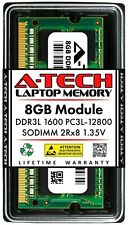
A-Tech 8GB DDR3 1600 PC3-12800 Laptop SODIMM 204-Pin Memory RAM PC3L DDR3L 1x 8G
$21.68
DDR4 Laptop RAM 4GB 8GB 16GB 32GB 2400 2666 3200 Samsung Hynix
$66.00
Lot 500 SK hynix 16GB 2Rx8 PC4-23400 DDR4-2933Y ECC Registered Server Memory RAM
$47988.00
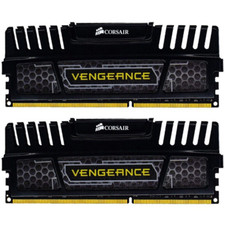
Corsair Vengeance DDR3 8GB 16GB 32GB 1866MHz PC3-14900 Desktop RAM Memory DIMM
$85.00
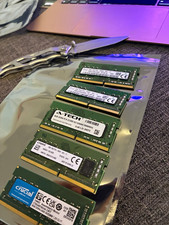
Lot of 5 - Mixed Brands 40GB (5x8GB) DDR4-2666 PC4-21300 SO-DIMM 260-Pin Non-ECC
$150.00
|
||
|
No Discussions have been posted on this vulnerability. |