|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-285: sane Vulnerability Assessment Details
|
RHSA-2003-285: sane |
||
|
Check for the version of the sane packages Detailed Explanation for this Vulnerability Assessment Updated SANE packages that resolve a number of vulnerabilities with the saned daemon are now available. SANE is a package for using document scanners. Sane includes a daemon program (called saned) that enables a single machine connected to a scanner to be used remotely. This program contains several vulnerabilities. NOTE: Although the SANE packages include this program, it is not used by default under Red Hat Enterprise Linux. The IP address of the remote host is only checked after the first communication occurs, causing saned.conf restrictions to be ineffective for the first communication. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0773 to this issue. A connection that is dropped early causes one of several problems. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2003-0774, CVE-2003-0775, and CVE-2003-0777 to these issues. Lack of error checking can cause various other unfavorable consequences. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the names CVE-2003-0776 and CVE-2003-0778 to these issues. Users of SANE (particularly those that use saned for remote scanner access) should upgrade to these errata packages, which contain a backported security patch to resolve these issues. Solution : http://rhn.redhat.com/errata/RHSA-2003-285.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

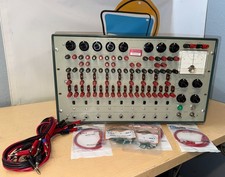
Refurbished Working 1960's Heathkit EC-1 Educational Electronic Analog Computer
$2999.99
Vintage George A Philbrick Researches Tube Analog Computer Module Serial 005503
$109.99
1969 EAI TR-20 Analog Computer Programming PACE Philbrick Electronic Associates
$36.00
Vintage 1970’s Analogic MP2110 10-Bit A/D Converter Computer Circuit Board
$24.99
Extron RGB-160XI Analog Computer Video 60-378-01
$127.06
Vintage Goodyear Electronic GEDA Analog Computer Plug -- Extremely Rare
$179.00
VINTAGE 1970s SKIT Scientific Kit for Computer & Electronics SEALED INSIDE Rare
$380.00
Vintage Analog Computing Magazines For Atari Computer Owners No 11-20 Acceptable
$75.00
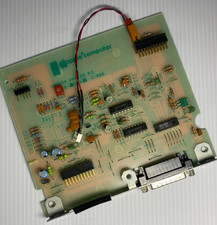
VINTAGE Apple Unidisk Analog Card - Circa 1986 | P/N 820-0190-A
$22.67
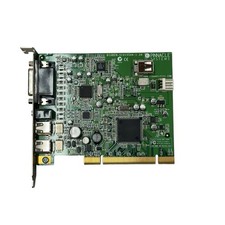
Pinnacle Systems GmbH BigBen-51015544-1.2A PCI Video Capture Card
$26.21
|
||
|
No Discussions have been posted on this vulnerability. |