|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-270: kdebase Vulnerability Assessment Details
|
RHSA-2003-270: kdebase |
||
|
Check for the version of the kdebase packages Detailed Explanation for this Vulnerability Assessment Updated KDE packages that resolve a local security issue with KDM PAM support and weak session cookie generation are now available. KDE is a graphical desktop environment for the X Window System. KDE between versions 2.2.0 and 3.1.3 inclusive contain a bug in the KDE Display Manager (KDM) when checking the result of a pam_setcred() call. If an error condition is triggered by the installed PAM modules, KDM might grant local root access to any user with valid login credentials. It has been reported that one way to trigger this bug is by having a certain configuration of the MIT pam_krb5 module that leaves a session alive and gives root access to a regular user. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0690 to this issue. In addition, the session cookie generation algorithm used by KDM was considered too weak to supply a full 128 bits of entropy. This could make it possible for non-authorized users, who are able to bypass any host restrictions, to brute-force the session cookie and gain access to the current session. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0692 to this issue. Users of KDE are advised to upgrade to these erratum packages, which contain security patches correcting these issues. Red Hat would like to thank the KDE team for notifying us of this issue and providing the security patches. Solution : http://rhn.redhat.com/errata/RHSA-2003-270.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

Windows XP, Vista, 8.1, Linux Knoppix, Office XP, (6 CDS)
$10.00
KNOPPIX 9.1 Linux Install & Live DVD 32bit & 64bit
$19.99
KNOPPIX USB DVD OS , BEST OF ALL HIGHLY RECOMENDED
$11.99
Knoppix Live GNU Linux System 9.1 on Bootable CD / DVD / USB Flash Drive
$5.99
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 16G USB Stick
$20.85
$8.00

VINTAGE SOFTWARE | KNOPPIX STD 0.1 (SECURITY TOOLS DISTRIBUTION)
$7.57
Knoppix Linux Bootable OS v8.6 "Original Live Operating System" 32G USB Stick
$21.42
$7.00
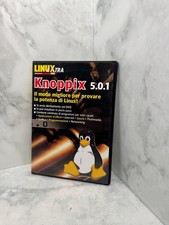
Knoppix 5.0.1 ULTRA RARE Linux DVD - Linux Pro Extra August 2006
$33.98
|
||
|
No Discussions have been posted on this vulnerability. |