|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-195: kernel Vulnerability Assessment Details
|
RHSA-2003-195: kernel |
||
|
Check for the version of the kernel packages Detailed Explanation for this Vulnerability Assessment Updated kernel packages for Red Hat Enterprise Linux are now available which address several security vulnerabilities. The Linux kernel handles the basic functions of the operating system. Several security issues have been found that affect the Linux kernel: Al Viro found a security issue in the tty layer whereby any user could cause a kernel oops. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0247 to this issue. Andrea Arcangeli found an issue in the low-level mxcsr code in which a malformed address would leave garbage in cpu state registers. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0248 to this issue. The TCP/IP fragment reassembly handling permits remote attackers to cause a denial of service (CPU consumption) via packets that cause a large number of hash table collisions, a vulnerability similar to CVE-2003-0244. The Common Vulnerabilities and Exposures project (cve.mitre.org) has assigned the name CVE-2003-0364 to this issue. These kernels also contain updated fixes for the ioperm security issue, as well as fixes for a number of bugs. It is recommended that users upgrade to these erratum kernels, which contain patches to correct these vulnerabilities. Solution : http://rhn.redhat.com/errata/RHSA-2003-195.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |

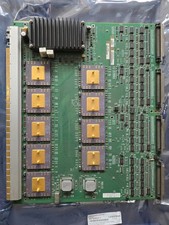
Vintage DEC E2052-AA AlphaServer I/O Board 9 Gold Ceramic ICs 4.3 LB Gold Scrap
$729.99
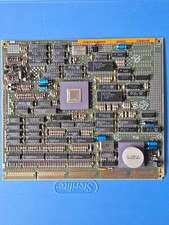
Vintage DEC Digital T1043 DWMBB/B VAXBI XMI Adapter 5018232-01 C1 VAX Board
$109.99
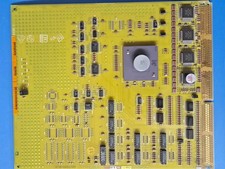
Vintage DEC Digital XMI-A1 5017293-01A1 LWPR BE3-0 VAX Circuit Board T2012
$74.99
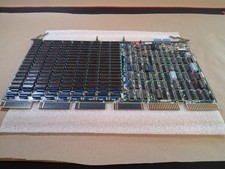
Vintage DEC/Mostek memory systems MK 8015 AA-00 6805-08015 1100 REV C(B7)
$279.99
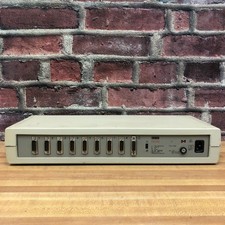
Vintage DEC Digital Equipment DELNI 8-Port Ethernet Local Network Hub VAXstation
$79.95
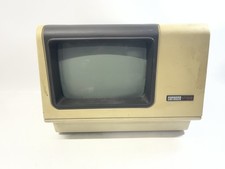
Vintage DEC VT100 Series Terminal (Powers On)
$499.99
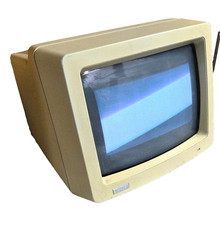
Vintage Digital VR241-A color CRT monitor, powers on, DEC Rainbow or terminal
$150.00
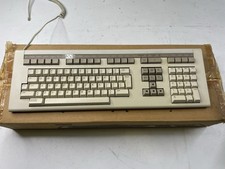
Vintage DEC LK201 Digital Equipment Corporation (DEC) LK201-AA Computer Keyboard
$149.99
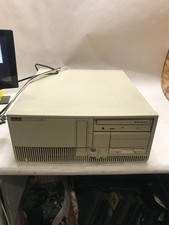
Vintage DEC Digital Starion 200 Desktop PC Powers On Boots To BIOS NO HDD - DW
$269.99
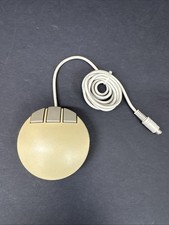
Vintage DEC Digital VSXXX-AA.B03 Hawley 3-Button Mouse 1986 Tested Working
$111.00
|
||
|
No Discussions have been posted on this vulnerability. |