|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Red Hat Local Security Checks >> RHSA-2003-058: shadow Vulnerability Assessment Details
|
RHSA-2003-058: shadow |
||
|
Check for the version of the shadow packages Detailed Explanation for this Vulnerability Assessment Updated shadow-utils packages are now available. These updated packages correct a bug that caused the useradd tool to create mail spools with incorrect permissions. The shadow-utils package includes programs for converting UNIX password files to the shadow password format, plus programs for managing user and group accounts. One of these programs is useradd, which is used to create or update new user information. When creating a user account, the version of useradd included in Red Hat packages creates a mail spool file with incorrectly-set group ownership. Instead of setting the file's group ownership to the "mail" group, it is set to the user's primary group. On systems where other users share the same primary group, this would permit those users to be able to read and write other user mailboxes. These errata packages contain an updated patch to useradd. Where a mail group exists, mailboxes will be created with group mail having read and write permissions. Otherwise the mailbox will be created without group read and write permissions. All users are advised to upgrade to these updated packages and also to check the /var/spool/mail directory to ensure that mailboxes have correct permissions. Solution : http://rhn.redhat.com/errata/RHSA-2003-058.html Network Security Threat Level: High Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2004 Tenable Network Security |
||
|
Cables, Connectors |


Crucial MX500 1TB 2.5" SATA III Internal SSD CT1000MX500SSD1
$99.99

Samsung 2.5" 870 EVO SSD SATA III 250GB 500GB 1TB Internet Solid State Drive Lot
$90.00
Samsung New SSD 970 EVO Plus 2TB 1TB 500GB 250GB NVMe M2 Internal Hard Drive Lot
$79.99
Netac 120GB 256GB 1TB 2TB Internal SSD 2.5'' SATAIII 6Gb/s Solid State Drive lot
$119.99

Netac 2TB 1TB 512GB 256GB Internal SSD 2.5inch SATAIII Solid State Drive lot
$549.00
Crucial MX500 250GB 2.5" SATA III SSD - Preowned
$29.00
Samsung 256 GB Internal SATA SSD Fully Tested 50%-79% Health
$24.00
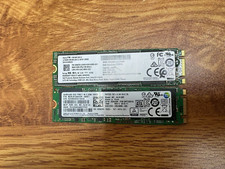
2 PACK 128 GB SSD M.2 2280 SATA Solid State Drive Major Brands, Samsung, LiteON
$28.00
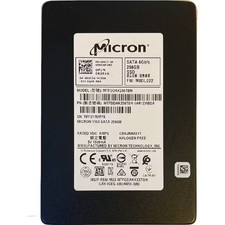
Micron MTFDDAK256TBN 256 GB, Internal ,2.5" SSD
$23.00
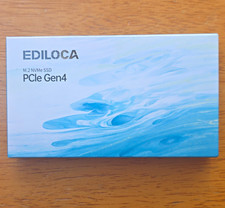
EDILOCA EN880E 1TB M.2 NVMe PCIe Gen4 Internal SSD for Laptop/PC
$115.00
|
||
|
No Discussions have been posted on this vulnerability. |